Bob Group, the company behind online marketplace Bob Shop, has told customers to treat their card details as exposed after an attacker breached its systems and copied encrypted card numbers along with the key needed to decrypt them.
In a notice emailed to customers on Thursday and seen by TechCentral, the company said an “unauthorised party” gained access to parts of its systems on 30 and 31 October. The attacker reached the Bob Shop database that holds customer and seller accounts and “older partial payment records”. The last recorded activity was on 1 November.
The exposed card records include cardholders’ names, card numbers and expiry dates. “The card number was stored in encrypted form, but the encryption key was also copied, so the card number should be treated as exposed,” the company said. The records do not include card security codes (CVVs).
The attacker could also reach account details – names, email addresses, usernames and passwords, the last stored in hashed form. Bob Group said it had no evidence these were read, “but we cannot rule it out”.
The card number was stored in encrypted form, but the encryption key was also copied, so the card number should be treated as exposed.
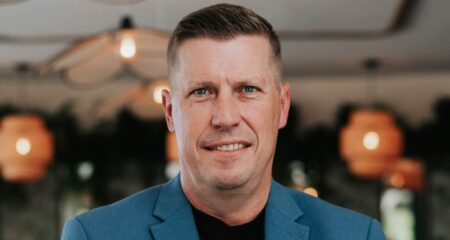
Bob Group CEO Anita Erasmus
The company does not yet know who was responsible. It said it had reported the breach to the Information Regulator, as the Protection of Personal Information Act (Popia) requires, and had told its acquiring bank, which was asked to notify the card schemes so that card issuers can watch for fraud.
The notice was signed by Anita Erasmus as information officer. She took over as CEO from co-founder Andy Higgins on 1 September. Bob Group was formed in 2022 from the merger of auction site Bidorbuy and logistics software firm uAfrica.
On 1 November, Bob Group said, it removed historical card numbers, names and expiry dates from the live Bob Shop database and replaced the encryption key. It has also closed the routes the attacker used, ended all active sessions and replaced exposed passwords, keys and system credentials.
It has put “more stringent approval processes on all payouts” and is holding “every change of payout bank details until it is confirmed”. Seller accounts were in the breached database, and the notice, sent to buyers who paid by card, does not say whether any seller payouts were affected. — (c) 2026 NewsCentral Media