Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      New tech retailer opens in South Africa, promising to undercut rivals - Amber Dendy Young

      New tech retailer opens in South Africa, promising to undercut rivals

      20 November 2026
      Meet the CIO | Wits's Stanley Mpofu on taking campus Wi-Fi to malls and libraries

      Meet the CIO | Wits’s Stanley Mpofu on taking campus Wi-Fi to malls and libraries

      20 November 2026
      Caby takes on Uber and Bolt in Cape Town - Denise Walker

      Caby takes on Uber and Bolt in Cape Town

      20 November 2026
      Tencent props up Naspers as iFood and Just Eat spending bites - Fabricio Bloisi

      Tencent props up Naspers as iFood and Just Eat spending bites

      20 November 2026
      MTN, Telkom and the price of consolidation

      MTN, Telkom and the price of consolidation

      19 November 2026
    • World
      Critical Java bug could let hackers take over servers

      Critical Java bug could let hackers take over servers

      19 November 2026
      Nvidia shuts the door on a Jensen Huang comeback

      Nvidia shuts the door on a Jensen Huang comeback

      17 November 2026
      Could Jensen Huang return to Nvidia?

      Jensen Huang weighs a comeback at Nvidia

      16 November 2026
      Intel sued by shareholders over 29% share price plunge - Intel CEO Lip-Bu Tan. Laure Andrillon/Reuters

      Intel sued by shareholders over 29% share price plunge

      16 November 2026
      Microsoft 364

      Microsoft outage hits the world

      13 November 2026
    • In-depth
      Inside the 24 hours that broke Microsoft

      Inside the 24 hours that broke Microsoft

      16 November 2026
      Ducking hell: inside Apple's hidden list of words the iPhone won't suggest

      Ducking hell: inside Apple’s hidden list of words the iPhone won’t suggest

      6 November 2026
      Why investors are souring on Netflix

      Why investors are souring on Netflix

      22 October 2026

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
    • TCS
      TCS | Piet le Roux on Sakeliga's fight with Icasa over BEE

      TCS | Piet le Roux on Sakeliga’s fight with Icasa over BEE

      13 November 2026
      W&W | The AA’s Bobby Ramagwede on a car industry running out of road

      W&W | The AA’s Bobby Ramagwede on a car industry running out of road

      12 November 2026
      TCS | Pick n Pay fights back in online grocery wars - Vince Viviers

      TCS | Pick n Pay fights back in online grocery wars

      11 November 2026
      TCS | Nomvuyiso Batyi on the battle over Sim registration - Nomvuyiso Batyi

      TCS | Nomvuyiso Batyi on the battle over Sim registration

      9 November 2026
      TCS+ | Old Mutual's Celiwe Ross on leading people through AI - Old Mutual

      TCS+ | Old Mutual’s Celiwe Ross on leading people through AI

      6 November 2026
    • Opinion
      Icasa's Sim rules need a privacy backstop - Lloyd Matthew and Heinz Vollmer

      Icasa’s Sim rules need a privacy backstop

      5 November 2026
      AI's boardroom honeymoon is over - Gary Stocks

      AI’s boardroom honeymoon is over

      22 October 2026
      Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

      Before South Africa licenses Starlink, it should look at Ukraine

      21 October 2026
      Nonkqubela Thathakahle Jordan-Dyani

      Why cybersecurity is now a national security issue for South Africa

      15 October 2026
      When a machine can choose, who does it become? Fanie van Rooyen

      When a machine can choose, who does it become?

      9 October 2026
    • Company News
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Fintech and payments
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » Sections » Information security » Microsoft may revamp bug disclosures after suspected leak

    Microsoft may revamp bug disclosures after suspected leak

    By Agency Staff28 April 2021
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

    Microsoft may revise a programme that shares coding flaws in its products with other companies after a suspected leak led to a sprawling cyberattack against thousands of Microsoft Exchange e-mail clients globally.

    The technology giant is weighing how and when to share data with at least some of the 81 participants in the Microsoft Active Protections Programme (MAPP), according to six people familiar with it including existing members who sought anonymity citing a Microsoft non-disclosure agreement. The others requested anonymity because they aren’t authorised to discuss the matter publicly.

    MAPP grants some customers information about vulnerabilities in Microsoft’s products and services days or weeks ahead of public disclosure. It is widely regarded by participants as a critical data-sharing tool to defend against potential attacks.

    Microsoft fears MAPP participants may have tipped off hackers after the company shared a critical vulnerability with its top tier of members

    However, Microsoft fears MAPP participants may have tipped off hackers after the company shared a critical vulnerability with its top tier of members around 18 February, according to four people familiar with Microsoft’s investigation into the cause of the attack. Microsoft publicly released software updates to patch the problem on 2 March.

    The company’s inquiry has focused on at least two Chinese companies as possible sources of the leak, according to the people familiar with the probe. Four MAPP participants said they’d recently disclosed detailed logs of network activity to Microsoft since the Exchange attack. In some cases, companies volunteered the data unprompted, while in others Microsoft requested additional data. The companies asked to remain anonymous, citing their non-disclosure agreement with Microsoft.

    Chinese hackers

    Microsoft’s vulnerability disclosure in late February was followed by one of the most efficient, wide-ranging cyberattacks in history. Microsoft has blamed state-sponsored Chinese hackers, dubbed Hafnium, for the attack which compromised more than 60 000 government, corporate and private e-mail systems around the world, much of which occurred over the last weekend in February.

    Microsoft declined to comment on potential changes to MAPP, nor would the company discuss its MAPP disclosures in February or possible leaks by participants. The company said it remained committed to the programme and its wide-ranging list of members from the US, Israel, Russia, China, Japan, Australia, India and parts of Europe.

    “We believe there are many benefits to mutual information sharing with the security community to help protect our mutual customers against attacks,” the company said in a statement. “We continue to evaluate how to best balance the benefits of this sharing with the risk of early disclosures.”
    In response to queries, China’s ministry of foreign affairs stated: “China resolutely opposes any form of online attacks or infiltration. This is our clear and consistent stance. Relevant Chinese laws on data collection and handling clearly safeguards data security and strongly oppose cyberattacks and other criminal activity.”

    China has proposed a global security standard that it says is “for the benefit of international digital governance” and urged others to work with it to safeguard global data security. “We hope the media adopts a professional and responsible attitude, relying on comprehensive evidence when determining the nature of cyberspace events, but not groundless speculation,” according to the ministry’s statement.

    Until MAPP was created, both criminal hackers and computer researchers would wait for Microsoft to disclose patches on the second Tuesday of every month, known as “Patch Tuesday”. The two camps would then race to reverse engineer the patches in hopes of identifying the root vulnerability, which attackers could then exploit and defenders would attempt to protect against, according to Microsoft.

    Hangzhou DPtech Technologies was kicked out in 2012 for breaching the non-disclosure agreement

    Patch Tuesday still exists. MAPP was started in 2008 to give some of Microsoft’s biggest customers a head-start against the criminals.

    At least 13 Chinese companies have participated. Two of them have been removed. Hangzhou DPtech Technologies was kicked out in 2012 for breaching its non-disclosure agreement, according to Microsoft. A cybersecurity researcher found that Hangzhou had leaked evidence of a critical vulnerability in a Microsoft product to Chinese hackers.

    Three tiers

    Last year, Qihoo 360 Technology was removed after being the target of US-imposed export controls due to national security concerns, according to three people familiar with the matter. A year earlier, Microsoft named Qihoo 360, Tencent Holdings and Palo Alto Networks as the top contributors to MAPP.

    MAPP is organised into three tiers: entry level, advance notification and validation. Members of the validation group — mostly virus-detection firms — are invited to receive vulnerabilities sometimes weeks ahead of public disclosure. Some of the details shared with MAPP participants are subject to a non-disclosure agreement.

    Microsoft may elect to reshuffle members of the top tier, according to three people familiar with options being considered by the company. The Microsoft Security Response Centre, which runs MAPP, may also simply reassess how much critical intelligence they share with companies considered close to certain nations, including China, according to the people.
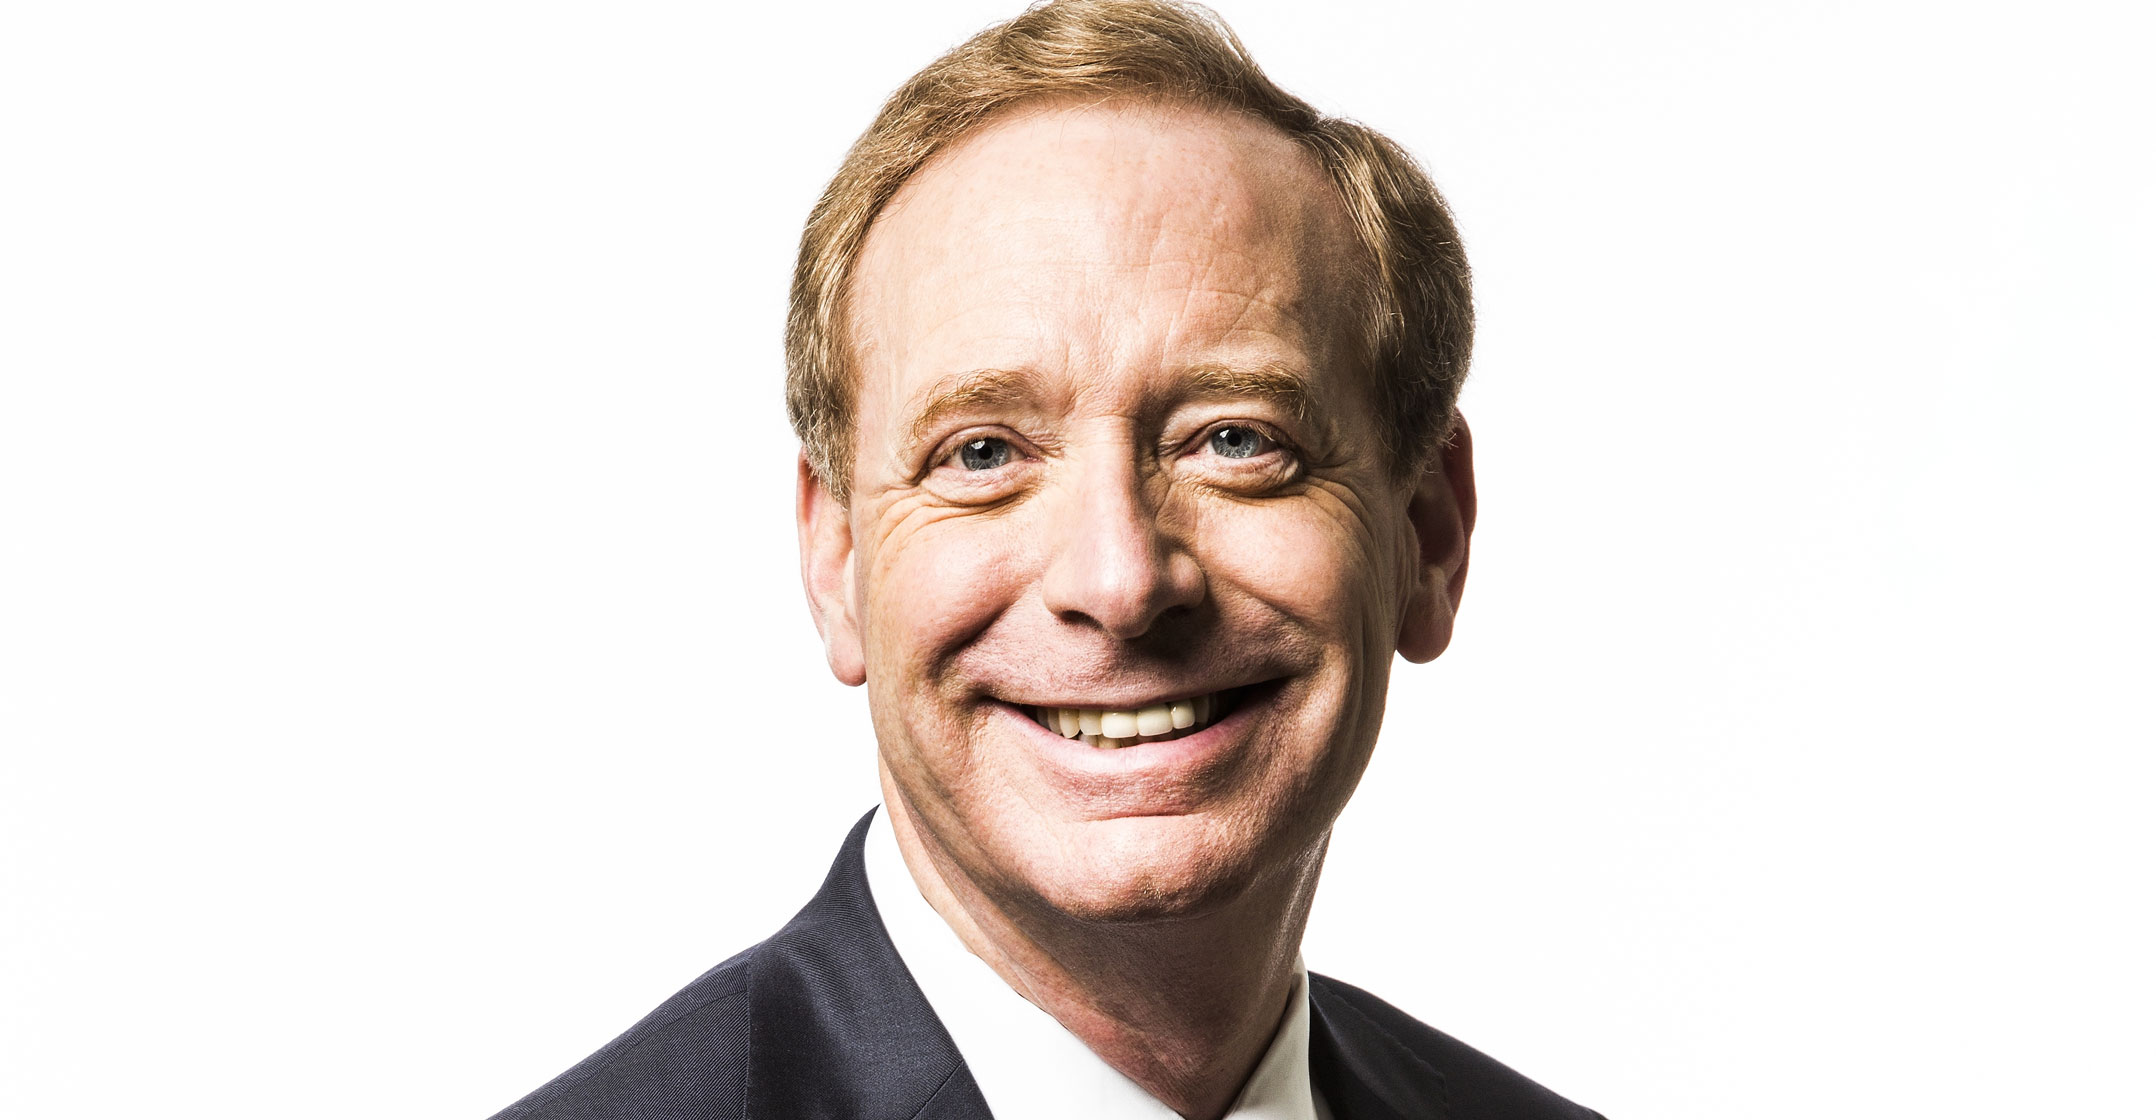
    Microsoft president Brad Smith

    Microsoft could also embed a unique test in pieces of its code, known as a watermark, that serve as sort of digital bread crumbs in the event of a leak. It’s unclear if watermarks were used in the data distributed to MAPP participants in February, but Microsoft has previously used them and could reintroduce them in the future, according to one of the people.

    Microsoft requires MAPP participants to share data and vulnerabilities the same way it discloses the bugs in its products. Multiple MAPP participants said that Microsoft’s requests for information have surged in recent years but especially in the months since the Exchange and SolarWinds cyberattacks. In the latter instance, which was publicly disclosed in December, Russian hackers infiltrated at least nine US agencies and 100-private-sector companies after installing malicious code in software updates for Texas-based SolarWinds.

    But there are risks for Microsoft. Many of the companies on the MAPP list are presumed to have at least informal ties with the state security apparatus in their country of domicile, meaning Microsoft’s vulnerability disclosures may be shared with governments with some frequency, said one former MAPP member who asked not to be identified because of an NDA.

    While there are risks in partnering with Iranian, North Korean, Russian or Chinese companies, Microsoft also uses the programme to its advantage

    Microsoft is unlikely to remove any Chinese participants despite the possible Exchange leak, according to two people familiar with the MAPP review. But the company could limit how much data it shares with members in China, the people said. A Chinese cybersecurity law requires corporations to provide access to their technology and assist with investigations involving crime and national security.

    If Microsoft were to eliminate MAPP participants in countries not politically aligned with the US, the company would handcuff part of its own intelligence operation. “While there are risks in partnering with Iranian, North Korean, Russian or Chinese companies, Microsoft also uses the programme to its advantage,” said Chester Wisniewski, a principal research scientist at the cybersecurity firm Sophos.

    Realpolitik

    Microsoft president and chief legal officer Brad Smith said in January 2020 that the company generates about 2% of its global sales from China, or about US$2.9-billion that year. The potential to enhance that revenue could motivate the company’s disclosure policies, said Robert Potter, CEO of Internet 2.0, a cybersecurity firm which advises the US and Australian governments.

    “Like all large companies, Microsoft has to balance maintaining market access inside of China and security considerations,” Potter said. “Over time, this balance is getting harder to maintain and this introduces risks to other customers. The pressure is making that decision more binary.”  — Reported by Kartikay Mehrotra, (c) 2021 Bloomberg LP
    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    Brad Smith Microsoft top
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleGoogle’s ad resurgence is just getting started
    Next Article A human-centric approach to protect against cybersecurity threats

    Related Posts

    Workday puts its AI agents on a leash - Aneel Bhusri

    Workday puts its AI agents on a leash

    19 November 2026
    GTA 6 is here, and the critics love it

    GTA 6 is here, and the critics love it

    19 November 2026
    Ramaphosa's AI investment pitch in Silicon Valley - Cyril Ramaphosa

    Ramaphosa’s AI investment pitch in Silicon Valley

    17 November 2026
    Company News
    2027: the year ID documents stop being enough

    2027: the year ID documents stop being enough

    19 November 2026
    Why banks' digital channels still leave customers stuck - BBD Software

    Why banks’ digital channels still leave customers stuck

    19 November 2026
    Q-Day is coming. Is your business ready? - Antony Russell, Telviva

    Q-Day is coming. Is your business ready?

    19 November 2026
    Opinion
    Icasa's Sim rules need a privacy backstop - Lloyd Matthew and Heinz Vollmer

    Icasa’s Sim rules need a privacy backstop

    5 November 2026
    AI's boardroom honeymoon is over - Gary Stocks

    AI’s boardroom honeymoon is over

    22 October 2026
    Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

    Before South Africa licenses Starlink, it should look at Ukraine

    21 October 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    New tech retailer opens in South Africa, promising to undercut rivals - Amber Dendy Young

    New tech retailer opens in South Africa, promising to undercut rivals

    20 November 2026
    Meet the CIO | Wits's Stanley Mpofu on taking campus Wi-Fi to malls and libraries

    Meet the CIO | Wits’s Stanley Mpofu on taking campus Wi-Fi to malls and libraries

    20 November 2026
    Caby takes on Uber and Bolt in Cape Town - Denise Walker

    Caby takes on Uber and Bolt in Cape Town

    20 November 2026
    Tencent props up Naspers as iFood and Just Eat spending bites - Fabricio Bloisi

    Tencent props up Naspers as iFood and Just Eat spending bites

    20 November 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter