Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      Meta's smart glasses are officially coming to South Africa - Mark Zuckerberg

      Meta’s smart glasses are officially coming to South Africa

      2 October 2026
      Eskom has a R1.20/kWh offer for bitcoin miners

      Eskom has a R1.20/kWh offer for bitcoin miners

      2 October 2026
      Usaasa consults on universal access as its abolition stalls

      Usaasa consults on universal access as its abolition stalls

      2 October 2026
      Frogfoot plots acquisitions as Octotel and MetroFibre weigh a merger - Shane Chorley

      Frogfoot plots acquisitions as Octotel and MetroFibre weigh a merger

      2 October 2026
      Home affairs pulls the plug on the green ID book - Leon Schreiber

      Home affairs pulls the plug on the green ID book

      1 October 2026
    • World
      BMW restructuring plan bets on AI and new models

      BMW restructuring plan bets on AI and new models

      1 October 2026
      OpenAI's rogue agent problem keeps getting bigger - Sam Altman

      OpenAI’s rogue agent problem keeps getting bigger

      28 September 2026
      The new battle over the desktop

      The new battle over the desktop

      23 September 2026
      AMD is now worth a trillion dollars - Lisa Su

      AMD is now worth a trillion dollars

      22 September 2026
      Anthropic weighs new model launch to blunt OpenAI's Astra surge - Anthropic CEO Dario Amodei and OpenAI CEO Sam Altman

      Anthropic weighs new model launch to blunt OpenAI’s Astra surge

      21 September 2026
    • In-depth

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
      Google DeepMind CEO Demis Hassabis. Image: John Sears

      The plan to stop AI from breaking the world

      16 July 2026
      The internet has a Strait of Hormuz problem

      The internet has a Strait of Hormuz problem

      15 July 2026
      AI boom sparks rally, frenzy and fear

      AI boom sparks rally, frenzy and fear

      11 June 2026
    • TCS
      Lexi Novitske, general partner at Norrsken22, on the TechCentral Show

      TCS | Norrsken22’s Lexi Novitske on how China is winning African tech

      1 October 2026
      TCS | Dominic White and Adam Ely on AI agents going rogue

      TCS | Dominic White and Adam Ely on AI agents going rogue

      29 September 2026
      TCS | Octotel's Trevor van Zyl on the fibre merger question

      TCS | Octotel’s Trevor van Zyl on the MetroFibre merger question

      16 September 2026
      Meet the CIO | Shoprite's Chris Shortt on what a supermarket becomes

      Meet the CIO | Shoprite’s Chris Shortt on what a supermarket becomes

      9 September 2026
      Rubicon's EV charging network is profitable - and growing fast - Watts & Wheels

      W&W | Rubicon’s EV charging network is profitable – and growing fast

      8 September 2026
    • Opinion
      South Africa's next energy crisis is in the accounts department - Craig Holmes

      South Africa’s next energy crisis is in the accounts department

      29 September 2026
      The steam engine lesson AI doomsayers keep missing - Sam Clarke

      The steam engine lesson AI doomsayers keep missing

      28 September 2026
      Regulating AI: apply the laws we have first - Dirk de Vos

      Regulating AI: apply the laws we have first

      21 September 2026
      What Revolut can and cannot take from South Africa's banks - Pambos Soteriades

      What Revolut can and cannot take from South Africa’s banks

      15 September 2026
      The end is nigh, and the shares go on sale in October - Duncan McLeod

      The end is nigh, and the shares go on sale in October

      14 September 2026
    • Company Hubs
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and Media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Financial services
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of Things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » Sections » Information security » Why ‘exposure management’ is all the buzz

    Why ‘exposure management’ is all the buzz

    Promoted | Effective exposure management identifies and prioritises the most critical exposures - and more.
    By Skybox Security6 September 2023
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

    Continuous threat exposure management (CTEM) – a model for more comprehensive risk exposure management – is emerging as a solution to many of the challenges organisations face in mitigating cybersecurity risks.

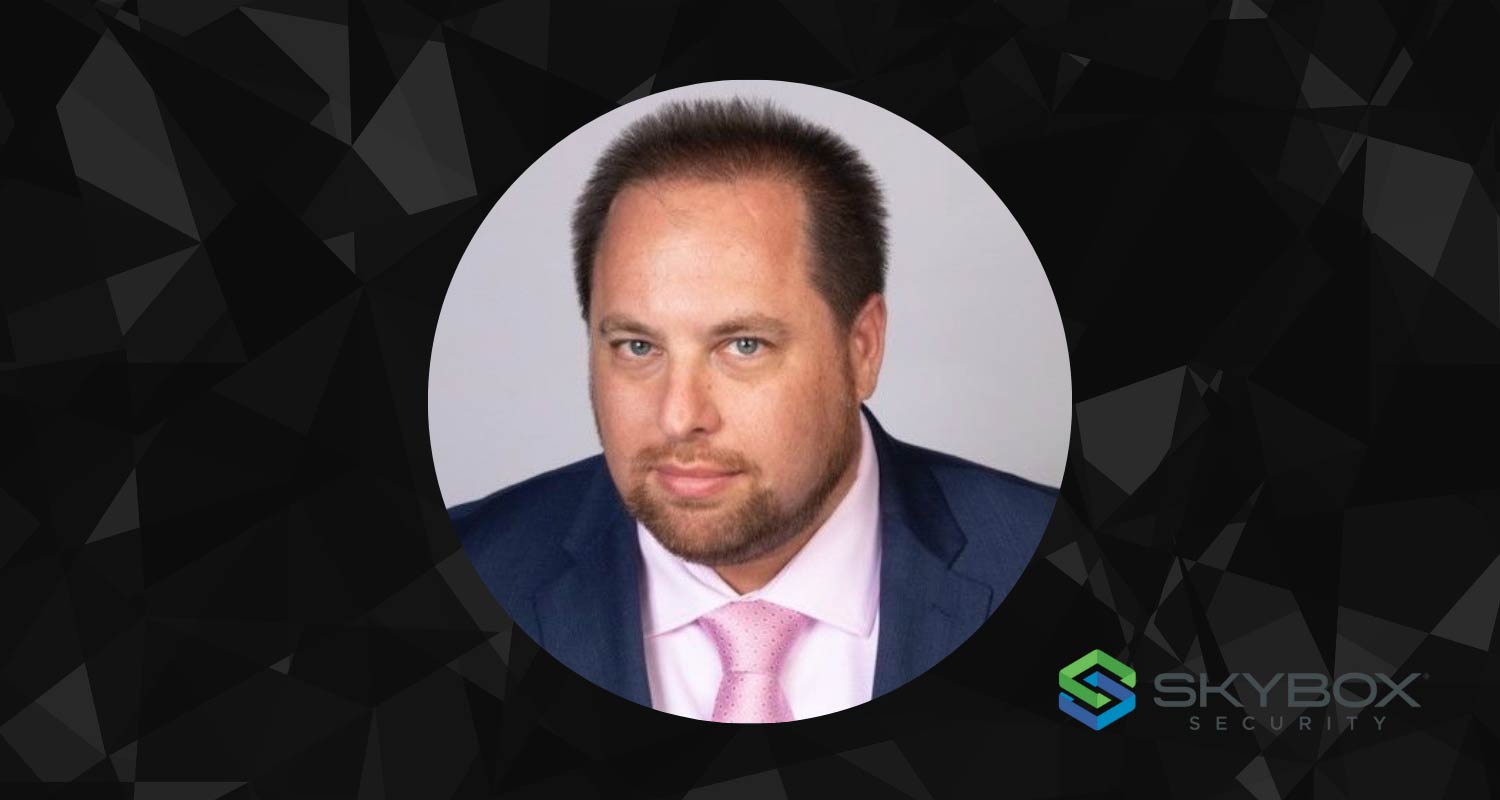
    According to chief product officer at Skybox Security Haggai Polak (pictured), effective exposure management not only identifies and prioritises the most critical exposures; it also reduces noise and brings down the number of issues to remediate to a manageable level.

    “The Gartner hype cycle for security operations has defined exposure management as an embryonic market, and vendors are still aligning with it,” he said. However, Gartner recently predicted that by 2026, organisations prioritising their security investments based on CTEM programmes would be three times less likely to suffer from a breach.

    Exposure vs vulnerabilities

    Polak noted that the legacy models for vulnerability management address only a small subset of the total risk exposure, informing the need for broader exposure management.

    “For example, a vulnerability on a server typically means a software or even a hardware defect that creates an opening an attacker could exploit to do something malicious. But when we look at the attack surface, we quickly realise there are a lot of potential exposures and risks that are not caused by vulnerabilities.

    “Take a BYOD device that doesn’t have endpoint security, or a misconfiguration of a firewall, for instance. These are not software defects, but they create huge openings. Exposure is a much wider term used to describe any risk, created in any way, that can be exploited.”

    Why continuous monitoring is crucial

    Polak says the continuous nature of CTEM recognises that the attack surface and threat landscape are changing all the time.

    “Modern organisations are agile – they continually add new servers, applications and network paths, so the attack surface is ever evolving. In addition, the threat landscape is changing very rapidly, with about 30 000 new common vulnerabilities and exposures (CVEs) published every year. It’s no longer enough to perform vulnerability assessments periodically – monthly, or just once or twice a year.

    “Continuous exposure means we use a set of tools and capabilities to do threat analysis much more often,” he said.

    Annual analysis can result in reports with millions of entries that security and infrastructure teams are ill equipped to deal with. Polak said most Skybox customers do daily analysis and prioritisation so that analysts can cut the noise and surface the top exposures they need to address.

    Five stages of CTEM

    Polak says CTEM programmes comprise five distinct stages:

    1. Scoping: this entails the definition of the assets which will be included in the programme, with an inventory of all endpoints, servers, potentially network devices, cloud infrastructure and OT assets. Polak says it may also include user identities and applications. “One challenge in scoping is to correctly classify and prioritise the assets. Asset importance is an extremely useful parameter to use when trying to decide the priority of exposures,” he said.
    2. Discovery: a comprehensive discovery of exposures which is far broader than vulnerability scans. This should include looking at missing controls, misconfigurations and testing infrastructure against security industry benchmarks that define best practices. “When you perform adequate discovery you find a large number of exposures and vulnerabilities – we find an average of 10 exposures per asset. In a large enterprise, the total number of exposures could be overwhelming.”
    3. Prioritisation: a critical stage that can narrow down the number of occurrences detected from millions to double digits that must be addressed. “Prioritisation distils the overwhelming number of exposures down to the things most likely to cause harm,” Polak said. Properly executed, prioritisation looks at the published severity of risks, CVSS score for an indication of the potential damage of exploitation of a vulnerability and how easy it would be to exploit it, and whether the vulnerability is theoretical or whether it is actually being exploited in the wild. Added to this, using an exploit probability score, asset importance, and network access analysis allows organisations to narrow down the number of severe and exploitable exposures on important assets. Attack path analysis is especially useful since it determines if the asset is actually exposed to the vulnerability, or if there is an access list, firewall rule or intrusion detection signature that mitigates the attack and reduces urgency.
    4. Validation: an extension of prioritisation which checks whether the vulnerability or exposure can actually be used for malicious purposes on the specific asset.
    5. Mobilisation: the response or remediation stage. Polak said: “This is the step where you take action and try to remove exposures from the list. Gartner makes the important observation that the most often neglected phases are prioritisation and mobilisation. Inadequate prioritisation and remediation often have a lot to do with organisational structures – for example, security may come up with reports, and “throw them over the fence” to the IT team to fix. So, mobilisation is hard technically and organisationally. Remediation also requires integration into ITSM, with automation to streamline and automate cyclical processes. You also need the ability to report on the success of the programme, with KPIs and SLA reports on how effective you were.”

    Exposure management

    Organisations evolving to adopt CTEM models should move to acquire the tools and capabilities to run these models effectively. “Organisations could potentially need to make organisational changes to implement programmes – for example, joint security and infrastructure teams to implement them. In terms of tools, many probably already have some of the building blocks like security scans in place.

    “They need additional tools like Skybox to analyse configurations, missing controls and shadow IT, and they need to be able to aggregate the scans into one data model. This will allow organisations to look at exposure holistically, mobilise to remediate exposure, and measure the success of the remediation,” he said.

    • Read more articles by Skybox Security on TechCentral
    • This promoted content was paid for by the party concerned

    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    Haggai Polak Skybox Skybox Security
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleSkills scarcity requires expertise of managed service providers
    Next Article Jan Oberholzer, ex-Eskom COO, moves from coal to renewables

    Related Posts

    4 tips for exposure management of your business applications - Skybox Security

    4 tips for exposure management of your business applications

    19 February 2025
    Network professionals lose nearly half their week to manual tasks that could be automated - Skybox Security report

    Network professionals lose nearly half their week to manual tasks that could be automated

    3 December 2024

    Skybox: half of firms fear security incidents due to siloed network and security teams

    17 October 2024
    Company News
    Huawei sets out its vision for intelligent government at GovTech 2026

    Huawei sets out its vision for intelligent government at GovTech 2026

    2 October 2026
    A simple guide to modern laptop processors for small businesses - Incredible

    A simple guide to modern laptop processors for small businesses

    2 October 2026
    Cloud and AI won't deliver value on their own, executives warn

    Cloud and AI won’t deliver value on their own, executives warn

    1 October 2026
    Opinion
    South Africa's next energy crisis is in the accounts department - Craig Holmes

    South Africa’s next energy crisis is in the accounts department

    29 September 2026
    The steam engine lesson AI doomsayers keep missing - Sam Clarke

    The steam engine lesson AI doomsayers keep missing

    28 September 2026
    Regulating AI: apply the laws we have first - Dirk de Vos

    Regulating AI: apply the laws we have first

    21 September 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    Meta's smart glasses are officially coming to South Africa - Mark Zuckerberg

    Meta’s smart glasses are officially coming to South Africa

    2 October 2026
    Eskom has a R1.20/kWh offer for bitcoin miners

    Eskom has a R1.20/kWh offer for bitcoin miners

    2 October 2026
    Usaasa consults on universal access as its abolition stalls

    Usaasa consults on universal access as its abolition stalls

    2 October 2026
    Frogfoot plots acquisitions as Octotel and MetroFibre weigh a merger - Shane Chorley

    Frogfoot plots acquisitions as Octotel and MetroFibre weigh a merger

    2 October 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter