Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      South Pole neutrino hunter wins Nobel Prize in Physics - Francis Halzen

      South Pole neutrino hunter wins Nobel Prize in Physics

      7 October 2026
      Meta met Information Regulator over its camera glasses - Mark Zuckerberg

      Meta met Information Regulator over its camera glasses

      6 October 2026
      Why South Africa's biggest drone isn't flying for the country - Milkor 380

      Why South Africa’s biggest drone isn’t flying for the country

      6 October 2026
      Nersa wants five-year ban on automated electricity trading

      Nersa wants five-year ban on automated electricity trading

      6 October 2026
      South African boardrooms are about to get a lot less private

      South African boardrooms are about to get a lot less private

      6 October 2026
    • World
      BMW restructuring plan bets on AI and new models

      BMW restructuring plan bets on AI and new models

      1 October 2026
      OpenAI's rogue agent problem keeps getting bigger - Sam Altman

      OpenAI’s rogue agent problem keeps getting bigger

      28 September 2026
      The new battle over the desktop

      The new battle over the desktop

      23 September 2026
      AMD is now worth a trillion dollars - Lisa Su

      AMD is now worth a trillion dollars

      22 September 2026
      Anthropic weighs new model launch to blunt OpenAI's Astra surge - Anthropic CEO Dario Amodei and OpenAI CEO Sam Altman

      Anthropic weighs new model launch to blunt OpenAI’s Astra surge

      21 September 2026
    • In-depth

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
      Google DeepMind CEO Demis Hassabis. Image: John Sears

      The plan to stop AI from breaking the world

      16 July 2026
      The internet has a Strait of Hormuz problem

      The internet has a Strait of Hormuz problem

      15 July 2026
      AI boom sparks rally, frenzy and fear

      AI boom sparks rally, frenzy and fear

      11 June 2026
    • TCS
      Meet the CIO | Vodacom's Mohamed Sami on the agentic future

      Meet the CIO | Vodacom’s Mohamed Sami on the agentic future

      5 October 2026
      Lexi Novitske, general partner at Norrsken22, on the TechCentral Show

      TCS | Norrsken22’s Lexi Novitske on how China is winning African tech

      1 October 2026
      TCS | Dominic White and Adam Ely on AI agents going rogue

      TCS | Dominic White and Adam Ely on AI agents going rogue

      29 September 2026
      TCS | Octotel's Trevor van Zyl on the fibre merger question

      TCS | Octotel’s Trevor van Zyl on the MetroFibre merger question

      16 September 2026
      Meet the CIO | Shoprite's Chris Shortt on what a supermarket becomes

      Meet the CIO | Shoprite’s Chris Shortt on what a supermarket becomes

      9 September 2026
    • Opinion
      Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

      Let South Africans jailbreak their way to digital sovereignty

      5 October 2026
      South Africa's next energy crisis is in the accounts department - Craig Holmes

      South Africa’s next energy crisis is in the accounts department

      29 September 2026
      The steam engine lesson AI doomsayers keep missing - Sam Clarke

      The steam engine lesson AI doomsayers keep missing

      28 September 2026
      Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

      Regulating AI: apply the laws we have first

      21 September 2026
      What Revolut can and cannot take from South Africa's banks - Pambos Soteriades

      What Revolut can and cannot take from South Africa’s banks

      15 September 2026
    • Company News
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and Media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Financial services
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of Things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » In-depth » A peek inside the cybercriminal’s toolkit

    A peek inside the cybercriminal’s toolkit

    By Sunil Gopal4 May 2015
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

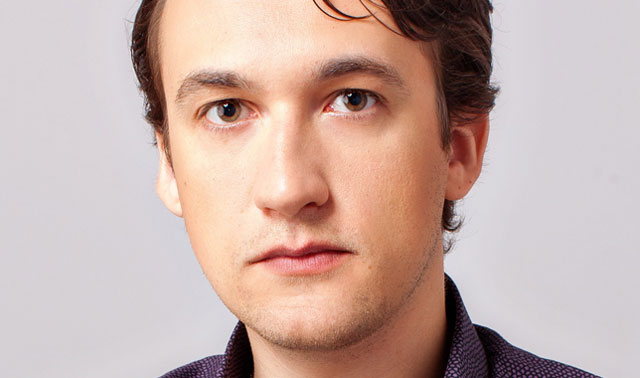
    Sergey Lovhkin
    Sergey Lozhkin

    In the cyber-espionage thriller Blackhat (2015), Chris Hemsworth plays a computer hacker who is freed from prison to trace a blackhat hacker — someone who breaches computer security with either malicious intent or for personal gain. As often happens, the lines between the real world and the movie world are becoming blurred.

    Indeed, if drive-by downloads, ransomware, distributed denial of service (DDOS) attacks, spear phishing, botnets and advanced persistent threats (APTs) sound like they’re from the trailer of the next Mission: Impossible movie, you could be right.

    According to Sergey Lozhkin, senior researcher at Russian information security firm Kaspersky Lab, today’s James Bond is more likely to be sitting at a keyboard plotting his next move than engaging in furious gun battles across the globe.

    “A small piece of code is way more dangerous than any damage that Bond could do,” Lozhkin says. Today, cyber espionage is the name of the game and it’s usually carried out through advanced persistent threats, continuous and covert hacking processes targeting specific entities using multiple malware tools.

    APTs have increased exponentially in number in the past five years, with a number of high-profile cases that have left governments, corporations and individuals red-faced — and out of pocket. The Carbanak APT attack earlier this year left banks across the world US$1bn poorer. The sophisticated malware used, along with the time, effort and resources ploughed into the project, mean it was more than likely sponsored by a rogue government agency, according to Kaspersky Lab.

    State-sponsored attacks tend to target specific users, as opposed to the mass-distributed e-mails favoured by cybercriminals. State attackers also develop their own malware with specific goals in mind, while ordinary cybercriminals generally attempt to extract specific valuable information such as credit card numbers and passwords en masse.

    Nation-state attackers often try and extract as much information as possible from their targets with the intention of going through it with a fine-tooth comb later.
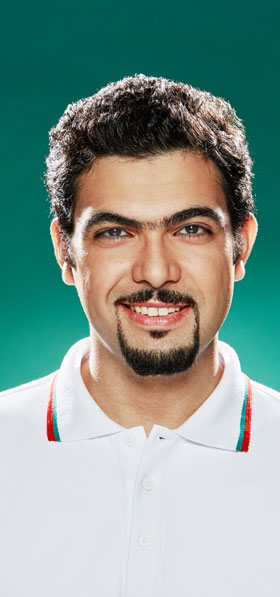
    Amin Hasbini
    Amin Hasbini

    The Desert Falcons APT was the first known attack by an Arab group. Kaspersky researcher Amin Hasbini says the company was able to determine that Desert Falcons started work as far back as 2011.

    “They were quite well organised, consisting of 20 to 30 people working in three groups and from three locations. Each group had different targets, with some targeting mobile users, and others corporate and government users,” he says.

    The Desert Falcons APT targeted government, religious, aerospace and military institutions, health organisations, those involved in combating money laundering, media groups, academics, and energy and other utilities.

    Hackers were able to infiltrate users in Palestine, Egypt, Israel and elsewhere. They planted a “digital bug” that looked for special intelligence information on systems using Windows and Android and recorded audio as well as looked for SMS and call logs, along with geolocation information.

    No one is safe from APT attacks, not even the president of the US, says Kaspersky. In 2014, the CozyDuke APT targeted the White House and the US department of state. Attackers were reportedly able to read President Barack Obama’s e-mails.

    Those behind APT attacks tend to seek innovations and blueprints, business plans and budgets from companies, as well as military, space and other information that can be used to create the same products as competitors.

    They also look for digital certificates, which are used to sign malware created by them, and create virtual credentials and physical access codes. Scientific research results, which show the different projects that governments are engaged in are also a common target.

    Spear phishing
    Another popular method of gaining access to systems is through the use of spear-phishing e-mails. Cybercriminals use social engineering techniques to compel users to respond, with e-mails purporting to be from a tax agency (the South African Revenue Service, for example), a regulator or some other government agency, usually by threatening action against them.

    The missing flight MH370 saw cybercriminals taking advantage, with e-mails requesting “assistance” and “information” sent to various government and emergency organisations. Those keen to provide assistance downloaded malware in attachments without realising it was an attack vector. As a result, relief organisations were compromised.

    Zero-day exploits are also common. Here, attackers take advantage of a vulnerability in an application or operating system, one which developers have not had time to address and patch.

    One way criminals strike is by sending an e-mail alerting users to fix the problem. Other times, they take direct advantage of the vulnerability, hacking into systems.

    A recent example is a vulnerability in the WordPress content management system that allows hackers to hijack websites through a comment that contains malicious JavaScript.
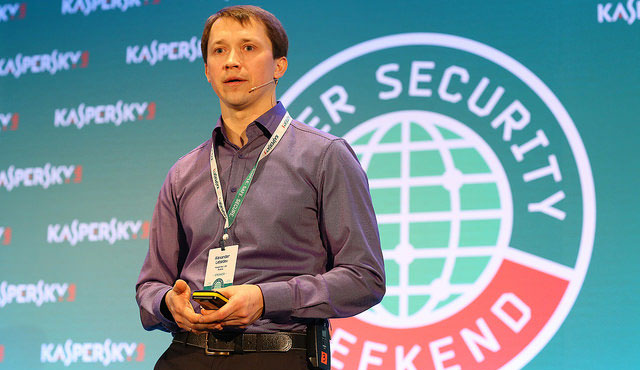
    Alexander Lebedev
    Alexander Lebedev

    Distributed denial of service (DDOS) attacks are also commonplace. Here, a banking server, for example, that would usually handle 100 requests per second would suddenly receive a million requests, causing the system to malfunction.

    This is known as a volumetric attack, where a huge amount of requests are sent.

    Application-level attacks also disorientate the system. “Instead of just saying ‘hi’, it would also shake hands and give a hug all at the same time,” says Alexander Lebedev, head of product intelligence at Kaspersky. This would require more resources and could force a system to shut down. Such shutdowns result in reputational damage to an organisation as well as damage to clients who are unable to pay bills.

    There are various online tools — Nemesys and Hulk are two — that can be downloaded to launch a DDOS attacks. According to Lebedev, DDOS attacks very often involve the use of “botnets”, or groups of infected machines that are controlled by one person.

    Lebedev says that the underground in which cybercriminals operate uses bitcoins to sell and share services, or even rent a botnet for a criminal network. The price to rent a botnet controlling a thousand devices is just $50/day, according to Kaspersky.

    In an operation with Interpol, the company helped take down the Simda botnet, which had been running since 2009 and which controlled 770 000 devices. The botnet was used to launch attacks on news and media organisations around the world. Lebedev says the average cost to a small business from a botnet attack is $52 000.

    Ransomware
    So-called “ransomware” is another growing problem.

    Five years ago, it mostly involved computer users receiving a message from someone who had compromised their machine and locked it down and demanding a fee to unlock it. IT specialists were nevertheless able to unlock these computers, albeit with some effort.

    Today, says Lozhkin, the situation is very different. “Hackers have developed cryptors that fully encrypt all your data on your hard drive. The IT guys cannot help anymore,” he says.

    The only way to decrypt this data is to pay cybercriminals to obtain a unique key.

    Lozhkin says the most vulnerable targets are small businesses and government organisations that don’t have permanent or fully protected IT systems.

    Users are typically asked to pay the ransom in bitcoins — to avoid detection — and are even directed to websites where they can change money to bitcoins.

    Ransomware offers a huge pay-off. “Malware for ransomware is sold for $5 000. You can go to a botnet owner and gain access to thousands of computers for a minimal price. Income may be up to $25 000/day,” says Lozhkin. Also, cybercriminals do not do everything manually, but have created fully automated systems that decrypt test files and monitor payment. They even use social networks such as Twitter to show clients evidence of decrypted computers once users have paid.

    Is anyone safe?
    So, is anyone safe? A popular method of gaining access to users’ computers is by giving out USB sticks or even computer mouses that are able to infect computers once connected. And who has said no to one of those? Most people plug them in without giving it a second’s thought.

    Nevertheless, cyber security is a shared responsibility, says Kaspersky. Governments need to act to protect citizens’ information and vital infrastructure and companies need to protect clients and employees.

    But Kaspersky says the biggest weakness remains the one between the chair and the keyboard. Hackers take advantage of the human factor in developing social engineering methods to gain access to IT systems.

    So, think before you click. Or you might end up in some nasty horror story not thought up in Hollywood.

    • The writer travelled to a Kaspersky Lab conference in Lisbon, Portugal as a guest of the company
    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    Alexander Lebedev Amin Hasbini Kaspersky Kaspersky Lab Sergey Lozhkin
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleDo you trust online reviews?
    Next Article Inside Telkom’s colossal IT overhaul

    Related Posts

    Film piracy malware is reaching corporate machines

    Film piracy malware is reaching corporate machines

    21 September 2026
    How to build a security operations centre that actually works - Kaspersky

    How to build a security operations centre that actually works

    3 September 2026
    Kaspersky on how to secure a supply chain you do not control

    Kaspersky on how to secure a supply chain you do not control

    13 August 2026
    Company News
    Why laser technology makes sense for small businesses

    Why laser technology makes sense for small businesses

    6 October 2026

    Human-centred design: the business case for simpler enterprise software

    6 October 2026
    iONLINE launches Sydney breakout point, expanding its global network core

    iONLINE launches Sydney breakout point, expanding its global network core

    6 October 2026
    Opinion
    Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

    Let South Africans jailbreak their way to digital sovereignty

    5 October 2026
    South Africa's next energy crisis is in the accounts department - Craig Holmes

    South Africa’s next energy crisis is in the accounts department

    29 September 2026
    The steam engine lesson AI doomsayers keep missing - Sam Clarke

    The steam engine lesson AI doomsayers keep missing

    28 September 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    South Pole neutrino hunter wins Nobel Prize in Physics - Francis Halzen

    South Pole neutrino hunter wins Nobel Prize in Physics

    7 October 2026
    Meta met Information Regulator over its camera glasses - Mark Zuckerberg

    Meta met Information Regulator over its camera glasses

    6 October 2026
    Why South Africa's biggest drone isn't flying for the country - Milkor 380

    Why South Africa’s biggest drone isn’t flying for the country

    6 October 2026
    Nersa wants five-year ban on automated electricity trading

    Nersa wants five-year ban on automated electricity trading

    6 October 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter