Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      Icasa's fingerprint Sim plan runs into major telco resistance - Nomvuyiso Batyi, CEO of the Association of Comms & Technology

      Icasa’s fingerprint Sim plan runs into major telco resistance

      30 October 2026
      Binance hit by $6.3-billion hack, the biggest crypto heist ever

      Binance hit by $6.3-billion hack, the biggest crypto heist ever

      30 October 2026
      AI has started a tech 'supercycle', says Datatec's Jens Montanana

      AI has started a tech ‘supercycle’, says Datatec’s Jens Montanana

      29 October 2026
      Icasa wants your fingerprint before you can get a Sim card

      Icasa wants your fingerprint before you can get a Sim card

      29 October 2026
      South Africa's AI policy team is racing a 30 November deadline

      South Africa’s AI policy team is racing a 30 November deadline

      29 October 2026
    • World
      Alleged Israeli spy company heavily targeted Starlink users

      How online ads were used to hunt Starlink users

      28 October 2026
      Anthropic's IPO stands alone

      Anthropic’s IPO stands alone

      23 October 2026
      PHP flaws trigger global scramble as hackers pounce

      PHP flaws trigger global scramble as hackers pounce

      22 October 2026
      OpenAI turns the tables on Apple in trade secrets fight

      OpenAI turns the tables on Apple in trade secrets fight

      15 October 2026
      Google's Gemini 4 Argon is finally here

      Google’s Gemini 4 Argon is finally here

      14 October 2026
    • In-depth
      Why investors are souring on Netflix

      Why investors are souring on Netflix

      22 October 2026

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
      Google DeepMind CEO Demis Hassabis. Image: John Sears

      The plan to stop AI from breaking the world

      16 July 2026
      The internet has a Strait of Hormuz problem

      The internet has a Strait of Hormuz problem

      15 July 2026
    • TCS
      TCS+ | Vox on AI, data rules and omnichannel communication for SMEs

      TCS+ | Vox on AI, data rules and omnichannel communication for SMEs

      26 October 2026
      TCS | The Cape Town firm quietly connecting Eskom, Pep and 6 000 ATMs - Réan van Niekerk, Metacom

      TCS | The Cape Town firm quietly connecting Eskom, Pep and 6 000 ATMs

      23 October 2026
      TCS+ | Boards are underestimating the cost of a cyberattack, says Arctic Wolf - Jason Oehley and Andre Den Hond

      TCS+ | Boards are underestimating the cost of a cyberattack, says Arctic Wolf

      22 October 2026
      W&W | LDV's Gerhard Moolman on electric bakkies, fleet orders and 'school fees'

      W&W | LDV’s Gerhard Moolman on electric bakkies and fleets

      9 October 2026
      TCS | Frogfoot sees bigger fibre deals coming - TechCentral Show guests Abraham van der Merwe and Shane Chorley

      TCS | Frogfoot sees bigger fibre deals coming

      8 October 2026
    • Opinion
      AI's boardroom honeymoon is over - Gary Stocks

      AI’s boardroom honeymoon is over

      22 October 2026
      Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

      Before South Africa licenses Starlink, it should look at Ukraine

      21 October 2026
      Nonkqubela Thathakahle Jordan-Dyani

      Why cybersecurity is now a national security issue for South Africa

      15 October 2026
      When a machine can choose, who does it become? Fanie van Rooyen

      When a machine can choose, who does it become?

      9 October 2026
      Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

      Let South Africans jailbreak their way to digital sovereignty

      5 October 2026
    • Company News
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Fintech and payments
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » Sections » Information security » Anthropic’s Mythos is the cyberthreat every CISO feared

    Anthropic’s Mythos is the cyberthreat every CISO feared

    Mythos marks the moment AI-powered vulnerability discovery moved from theoretical threat to operational reality for defenders.
    By Jonathan Zanger9 April 2026
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

    Anthropic's Mythos is the cyberthreat every CISO feared

    Late last month, the industry learnt that Anthropic is developing Claude Capybara – also referred to internally as Mythos – a powerful new AI model with substantially improved capabilities in vulnerability discovery, exploit development and multi-step attack reasoning. The details emerged through a data leak rather than a formal launch, but the market response was unmistakable: AI has crossed a critical cybersecurity threshold.

    Frontier models are accelerating attack life cycles. They will allow attackers to identify and exploit vulnerabilities at a scale, speed and level of sophistication that until recently was the preserve of advanced nation state actors. For security leaders, this is both a warning and a call to action. It crystallises a trend that has been building for some time: the democratisation and industrialisation of cyberattacks.

    Mythos is the early signal of two profound shifts in the threat landscape.

    AI allows attackers to move from manual, artisanal operations to repeatable, automated attack pipelines

    The first is the democratisation of advanced attack capabilities. Techniques that once required elite threat actors or well-funded nation state teams will soon be accessible to low-skilled attackers with AI assistance.

    The paths are already clear: abuse frontier models directly, as the Chinese state-sponsored group that used Claude Code to infiltrate roughly 30 organisations last year did, or wait for the same capabilities to appear in open-source models where no usage policies or safety layers stand in the way.

    This fundamentally lowers the barrier to entry for sophisticated attacks. Organisations that once considered themselves safe because they were not obvious targets of nation state activity are now at risk from newly capable criminal groups armed with AI-powered tools.

    Industrialisation of cyberattacks

    The second shift is the industrialisation of cyberattacks. With continued advances in agentic AI, threat actors will be able to scan legacy and software-as-a-service technologies at unprecedented frequency and scale. The result will be a near-continuous flow of novel attack methods targeting enterprise systems, networks and employees.

    AI allows attackers to move from manual, artisanal operations to repeatable, automated attack pipelines. Attacks are becoming systematic, scalable and reproducible – more like software manufacturing than craft. This is the era of the AI attack factory.

    Read: South Africa Inc must wake up to quantum threat

    The convergence of these two forces produces a dangerous outcome: more attackers executing more sophisticated attacks, increasing both volume and velocity simultaneously. The time-to-exploit window is collapsing towards zero.

    We should all be alarmed by what the Mythos leak revealed, but we should not be surprised. Security researchers have long anticipated that advanced models would eventually demonstrate proficiency in code review, vulnerability discovery and reverse engineering, and that they would integrate with the tools and APIs that enable penetration testing and exploitation.
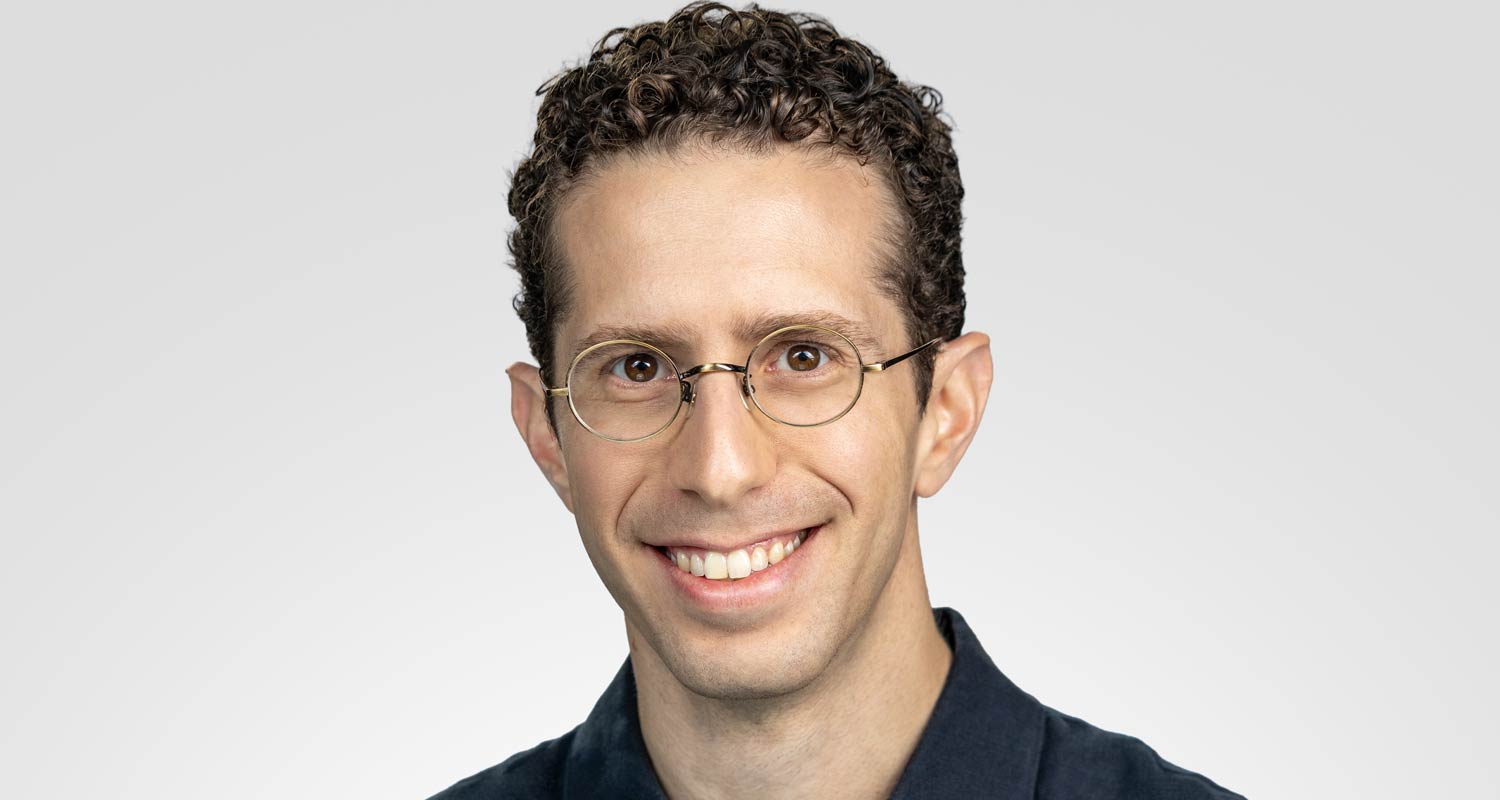
    The author, Check Point chief technology officer Jonathan Zanger
    The author, Check Point chief technology officer Jonathan Zanger

    The gap between writing code and analysing code is narrower than many realise. An AI system capable of generating sophisticated software can be trained or prompted to identify vulnerabilities within it. Combine that with exploit development and the ability to chain multi-step attacks, and you have an entirely new threat surface.

    In response to this evolving threat landscape, security leaders should conduct a rigorous reassessment of their foundations. This is not only about implementing new tools. It is about ensuring that existing tools are actually tuned for the threat that is now emerging.

    • A good starting point is to assess the efficacy of the first line of defence. Networks, firewalls, web application firewalls, endpoint protection and e-mail security are all critical, but are they tuned for zero-day protection? Default configurations are rarely optimised to defend against previously unknown exploits. If the perimeter and endpoint estate are running standard baselines, the exposure is real.
    • Next, evaluate vendor risk. Look hard at the CVE (common vulnerabilities and exposures) history of the security products on which the organisation depends. When AI compresses exploitation timelines to hours, a pattern of frequent critical vulnerabilities in a security vendor’s own products is no longer a manageable operational burden – it is a strategic liability.
    • Hunt the blind spots. Legacy servers, unpatched systems, accounts without multifactor authentication, unprotected remote access – the long tail of enterprise infrastructure is where attacks typically land.
    • Accelerate patching cycles and consider automated virtual patching and safe remediation. Time-to-patch becomes increasingly critical as campaign timelines move from weeks to minutes.
    • Finally, redefine and reinforce network segmentation to protect the crown jewels. Assume breach, limit lateral movement and ensure critical assets are isolated from general network traffic.

    What comes next

    The step change in AI models’ offensive capabilities has not happened in isolation. It has arrived alongside a sharp increase in open-source software supply-chain attacks, with both signals pointing to the same conclusion: the speed and surface area of attacks are accelerating.

    Whether an organisation has adopted AI or not is irrelevant. Threat actors have, and they will continue to push these capabilities further. New models will keep pushing the boundaries of what is possible, for defenders and attackers alike. That is not a surprise – it is the trajectory the industry has been tracking for years. What the recent disclosures make clear is that continuous reassessment is no longer optional.

    • The author, Jonathan Zanger, is chief technology officer of Check Point Software Technologies

    Get breaking news from TechCentral on WhatsApp. Sign up here.
    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    Anthropic Check Point Check Point Software Technologies Jonathan Zanger Mythos Mythos model
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleWhy South Africa’s EV market is going nowhere slowly
    Next Article Shoprite bakes AI into Sixty60 with Pixie launch

    Related Posts

    Companies rein in AI spending as running costs mount

    Companies rein in AI spending as running costs mount

    27 October 2026
    Anthropic's IPO filing lays bare the cost of the AI race - Dario Amodei

    Anthropic’s IPO filing lays bare the cost of the AI race

    26 October 2026
    Anthropic's IPO stands alone

    Anthropic’s IPO stands alone

    23 October 2026
    Company News
    Paratus continues to reshape connectivity in Namibia

    Paratus continues to reshape connectivity in Namibia

    29 October 2026
    Rate hikes threaten a household recovery built on cheaper credit - John Gellatly

    Rate hikes threaten a household recovery built on cheaper credit

    29 October 2026
    Choosing the right AI path for banks and large enterprises - Matthew Barnard BBD

    Choosing the right AI path for banks and large enterprises

    29 October 2026
    Opinion
    AI's boardroom honeymoon is over - Gary Stocks

    AI’s boardroom honeymoon is over

    22 October 2026
    Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

    Before South Africa licenses Starlink, it should look at Ukraine

    21 October 2026
    Nonkqubela Thathakahle Jordan-Dyani

    Why cybersecurity is now a national security issue for South Africa

    15 October 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    Icasa's fingerprint Sim plan runs into major telco resistance - Nomvuyiso Batyi, CEO of the Association of Comms & Technology

    Icasa’s fingerprint Sim plan runs into major telco resistance

    30 October 2026
    Binance hit by $6.3-billion hack, the biggest crypto heist ever

    Binance hit by $6.3-billion hack, the biggest crypto heist ever

    30 October 2026
    AI has started a tech 'supercycle', says Datatec's Jens Montanana

    AI has started a tech ‘supercycle’, says Datatec’s Jens Montanana

    29 October 2026
    Icasa wants your fingerprint before you can get a Sim card

    Icasa wants your fingerprint before you can get a Sim card

    29 October 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter