Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      Most of Datatec's R7-billion payout was taken in shares, not cash

      Most of Datatec’s R7-billion payout was taken in shares, not cash

      20 October 2026
      This is what an AI-run hacking spree looks like

      This is what an AI-run hacking spree looks like

      20 October 2026
      Post Office wants R2.2-billion from government as it braces for another loss

      Post Office wants R2.2-billion from government as it braces for another loss

      19 October 2026
      AI music is here and the rulebook is blank - Justin Erasmus

      AI music is here and the South African rulebook is blank

      19 October 2026
      SA start-up wants to put a padlock on your phone calls

      SA start-up wants to put a padlock on your phone calls

      19 October 2026
    • World
      OpenAI turns the tables on Apple in trade secrets fight

      OpenAI turns the tables on Apple in trade secrets fight

      15 October 2026
      Google's Gemini 4 Argon is finally here

      Google’s Gemini 4 Argon is finally here

      14 October 2026
      Apple's new HomeView smart home hub

      Apple takes another shot at the smart home

      13 October 2026
      AI is now holding up the world economy, says IMF

      AI is now propping up the world economy, says IMF

      12 October 2026
      SpaceX takes aim at US wireless carriers with spectrum acquisition

      Starlink is coming for your mobile operator

      9 October 2026
    • In-depth

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
      Google DeepMind CEO Demis Hassabis. Image: John Sears

      The plan to stop AI from breaking the world

      16 July 2026
      The internet has a Strait of Hormuz problem

      The internet has a Strait of Hormuz problem

      15 July 2026
      AI boom sparks rally, frenzy and fear

      AI boom sparks rally, frenzy and fear

      11 June 2026
    • TCS
      W&W | LDV's Gerhard Moolman on electric bakkies, fleet orders and 'school fees'

      W&W | LDV’s Gerhard Moolman on electric bakkies and fleets

      9 October 2026
      TCS | Frogfoot sees bigger fibre deals coming - TechCentral Show guests Abraham van der Merwe and Shane Chorley

      TCS | Frogfoot sees bigger fibre deals coming

      8 October 2026
      Meet the CIO | Vodacom's Mohamed Sami on the agentic future

      Meet the CIO | Vodacom’s Mohamed Sami on the agentic future

      5 October 2026
      Lexi Novitske, general partner at Norrsken22, on the TechCentral Show

      TCS | Norrsken22’s Lexi Novitske on how China is winning African tech

      1 October 2026
      TCS | Dominic White and Adam Ely on AI agents going rogue

      TCS | Dominic White and Adam Ely on AI agents going rogue

      29 September 2026
    • Opinion
      Nonkqubela Thathakahle Jordan-Dyani

      Why cybersecurity is now a national security issue for South Africa

      15 October 2026
      When a machine can choose, who does it become? Fanie van Rooyen

      When a machine can choose, who does it become?

      9 October 2026
      Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

      Let South Africans jailbreak their way to digital sovereignty

      5 October 2026
      South Africa's next energy crisis is in the accounts department - Craig Holmes

      South Africa’s next energy crisis is in the accounts department

      29 September 2026
      The steam engine lesson AI doomsayers keep missing - Sam Clarke

      The steam engine lesson AI doomsayers keep missing

      28 September 2026
    • Company News
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Fintech and payments
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » Sections » Information security » The case for regulating cybersecurity service providers in Africa

    The case for regulating cybersecurity service providers in Africa

    Promoted | Cybersecurity firms get deep access to sensitive systems, but who checks they are competent?
    By CyberM830 September 2026
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

    You hire a cybersecurity company to protect your organisation. You give its team access to your networks, systems, security architecture and, in some cases, highly sensitive information. You may even give them permission to deliberately try to break into your systems to find vulnerabilities before criminals do. But who determines whether the people you have trusted to do this are actually competent? And when something goes wrong, who holds them accountable?

    These questions are becoming increasingly important as African governments, businesses, banks, telecommunications operators and other organisations rely more heavily on private cybersecurity service providers (CSSPs).

    Cybersecurity is no longer simply an IT support function. These companies can find themselves inside some of the most sensitive parts of an organisation’s digital environment.

    There isn’t a simple yes-or-no answer to whether cybersecurity service providers should be regulated

    So perhaps it is time we asked: who secures the securers?

    At CyberM8 Initiative NPC, we don’t believe there is a simple yes-or-no answer to whether cybersecurity service providers should be regulated.

    There is a strong argument for greater accountability. But there is also a very real danger that poorly designed regulation could make it harder for emerging cybersecurity companies to participate in the industry.

    And that is a conversation Africa needs to have.

    There is a public-interest question

    The Private Security Industry Regulatory Authority (PSiRA) believes there is a case for appropriate oversight, but cautions against simply applying traditional private security regulation to cybersecurity.

    PSiRA says: “Cybersecurity service providers are increasingly entrusted with access to sensitive information, critical systems and digital infrastructure. This creates a strong public-interest case for appropriate oversight, particularly in relation to competence, ethical conduct, accountability, vetting and minimum professional standards. However, regulation should not simply replicate traditional private security requirements in a highly specialised and rapidly evolving sector. An effective framework should be risk-based, proportionate and technology-neutral, recognise existing professional and international standards, and avoid unnecessary duplication between regulators. It should protect consumers, organisations and national interests while enabling innovation, skills development and investment. PSiRA’s position is that the development of such a framework requires continued consultation with government, cybersecurity professionals, industry, regulators and technical experts to determine the appropriate regulatory model and clearly define institutional roles and responsibilities.”

    That last point matters. The conversation shouldn’t simply be about whether we regulate. It should also be about how we regulate, what we regulate and who should be responsible for that regulation. Cybersecurity is a highly specialised and fast-moving industry. The rules governing it need to recognise that reality.

    Are our existing laws enough?

    South Africa already has legislation and regulatory frameworks dealing with cybersecurity, cybercrime and data protection. But do they go far enough when it comes to the companies actually providing cybersecurity services? Cyber-law expert Prof Sizwe Snail ka Mtuze of Snail Attorneys believes there is still a gap.

    He says: “South Africa’s current framework does not sufficiently regulate Cybersecurity Service Providers (CSPs) as a distinct profession. The National Cybersecurity Policy Framework (NCPF), now approximately 15 years old, requires modernisation to respond to today’s rapidly evolving cyber threat and technology landscape. While the Cybercrimes Act addresses unlawful conduct and POPIA establishes data-protection and security obligations, neither sets minimum competency requirements for CSPs. The Joint Standard on Cybersecurity and Cyber Resilience provides more specific requirements for financial institutions, but comparable sector-wide professional assurance remains limited. A dedicated, risk-based and proportionate framework is therefore needed, particularly for high-risk services such as penetration testing, incident response and managed security operations. Such regulation should establish competency requirements, minimum professional standards, a statutory duty of care, incident-reporting obligations, appropriate liability and effective oversight, while avoiding unnecessary barriers for SMMEs. For critical sectors, the gap between cybersecurity liability and professional assurance is increasingly untenable.”

    The reference to small, medium and micro enterprises is especially important to us at CyberM8.

    What happens to the small cybersecurity company?

    Part of CyberM8’s work focuses on developing cybersecurity SMMEs and helping emerging businesses participate in the digital economy. That experience makes us particularly interested in what regulation could mean for smaller cybersecurity companies.

    Africa needs more home-grown cybersecurity businesses. We need young cybersecurity professionals building companies. We need local intellectual property, locally developed solutions and African companies capable of securing African institutions. But a small cybersecurity company does not have the same legal, compliance and financial resources as a multinational technology company.

    Imagine an emerging cybersecurity business employing five highly skilled young professionals. They have the technical capability to deliver penetration testing, vulnerability assessments or managed security services, but suddenly need to navigate expensive licensing, multiple regulatory registrations, complex compliance requirements and recurring fees before they can compete.
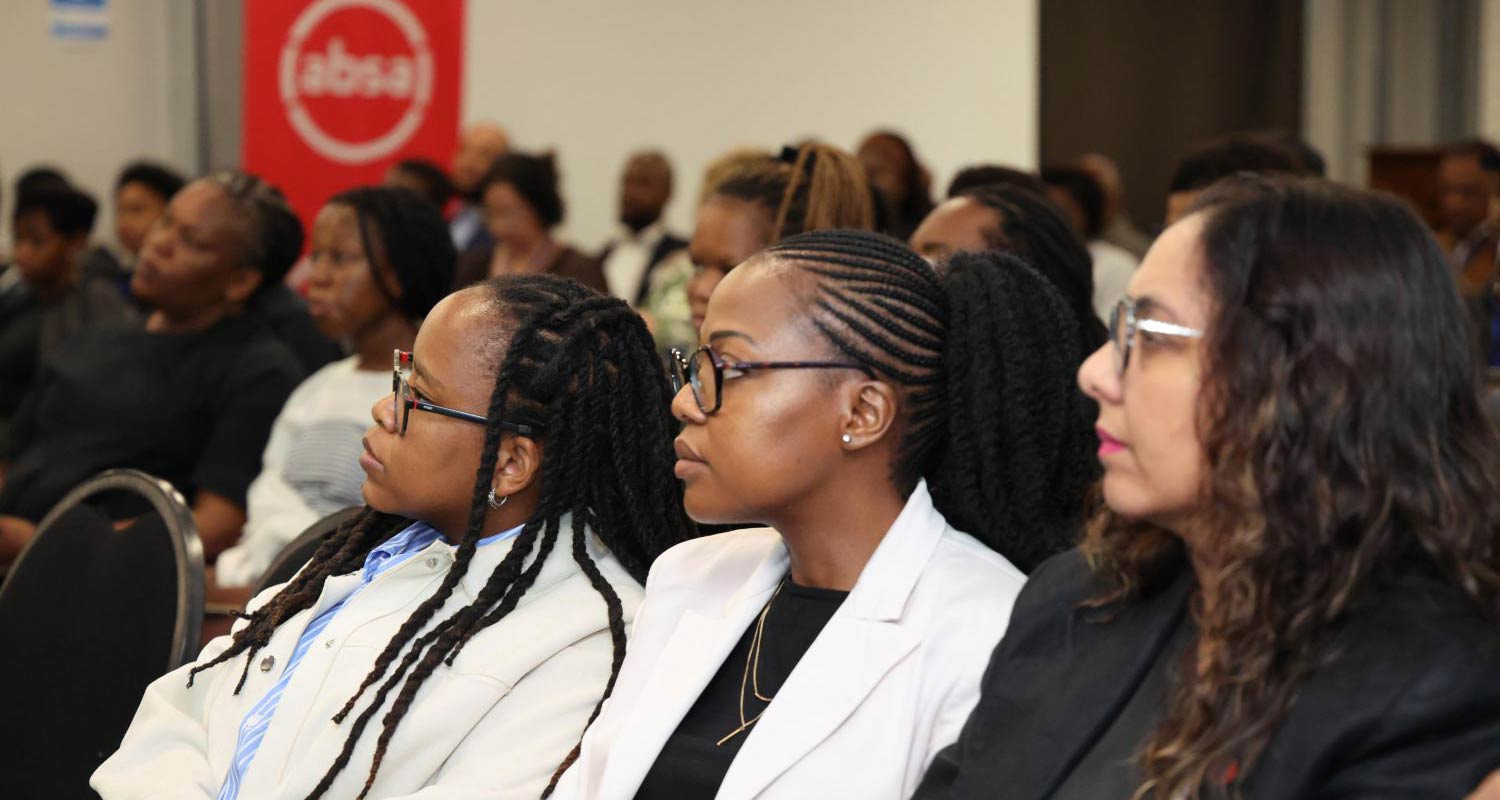
    Delegates listen during a CyberM8 Initiative cybersecurity session. As African organisations hand more of their security to private providers, the question of who holds those providers accountable is moving up the agenda. Image: Lerato Sepotokele/DCDT
    Delegates listen during a CyberM8 Initiative cybersecurity session. As African organisations hand more of their security to private providers, the question of who holds those providers accountable is moving up the agenda. Image: Lerato Sepotokele/DCDT

    We could unintentionally create a market where only large companies can afford to be cybersecurity companies. That cannot be the outcome. But neither should the alternative be a completely open environment where practically anyone can establish a company, call themselves a cybersecurity expert and be given access to sensitive systems. Somewhere between those two extremes is a conversation worth having.

    Perhaps the level of oversight should depend on the level of risk. Should someone delivering cybersecurity awareness training face exactly the same requirements as a company conducting penetration testing on critical infrastructure? Should a managed security operations centre responsible for monitoring government systems be treated in the same way as a small consultancy conducting basic cyber-risk assessments?

    These are not questions CyberM8 believes it should answer alone. They require the industry.

    Mozambique is already taking a different approach

    This is not only a South African conversation. Across the border, Mozambique is developing a much more explicit regulatory framework for cybersecurity providers.

    Mozambique’s Instituto Nacional de Tecnologias de Informação e Comunicação (INTIC) explains: “Mozambique is developing its legal and regulatory framework for building trust on cyberspace in the country. The Cybersecurity Law, the Cybercrime Law, the Data Center Regulation and the Cloud Computing Regulation, were recently published. The Cybersecurity Law introduces the registration and licensing of Cybersecurity Service Providers and defines INTIC as the National Cybersecurity Authority with responsibility in auditing and supervising cybersecurity service providers, both national and international. INTIC’s role includes the establishment of frameworks for accreditation and certification of cybersecurity professionals, and for the cybersecurity technical standards.”

    INTIC also points to the importance of cooperation beyond national borders: “INTIC, through the National CSIRT, participate on the international CSIRT networks such as the SADC CSIRT Committee, the ANCA and AfricaCERT at the continental level, and FIRST and ‘United Nations Cybersecurity Mechanism’ at the global level, with the aim of learning and contributing for better cooperation and collaboration in cross-border cybersecurity services provision, including the alignment on minimum standards, and professional competency requirements.”

    This raises an even bigger question for Africa.

    What happens when cybersecurity crosses the border?

    Imagine a cybersecurity company based in Johannesburg monitoring infrastructure for clients in Mozambique, Botswana and Kenya from one security operations centre.

    Which country’s requirements should apply? What happens if the provider is licensed in one country but not recognised in another? And what happens if 20 African countries eventually develop 20 completely different licensing regimes?

    Cybersecurity services are increasingly borderless. Regulation remains largely national. That tension is going to become harder to ignore. Perhaps Africa doesn’t need identical cybersecurity regulation in every country. But there may be value in discussing common minimum standards, professional competency, mutual recognition and cooperation between regulators.

    That discussion becomes even more important as African countries push for greater digital sovereignty while simultaneously building a more connected continental digital economy.

    This is exactly why we created the Africa Cybersecurity Indaba

    CyberM8’s position is deliberately in the middle. We understand why government, regulators and organisations responsible for critical systems would want greater assurance about the people and companies entrusted with protecting them.

    We also understand the entrepreneur trying to build a cybersecurity company with limited capital, compete for contracts, employ young people and establish credibility in a market where the barriers to entry are already significant.

    Both perspectives matter. That is one of the reasons we created the Africa Cybersecurity Indaba.

    The Indaba is intended to be a platform where government, regulators, cybersecurity companies, SMMEs, technology companies, academia, legal professionals, critical infrastructure operators and cybersecurity practitioners can sit around the same table and have these difficult conversations.
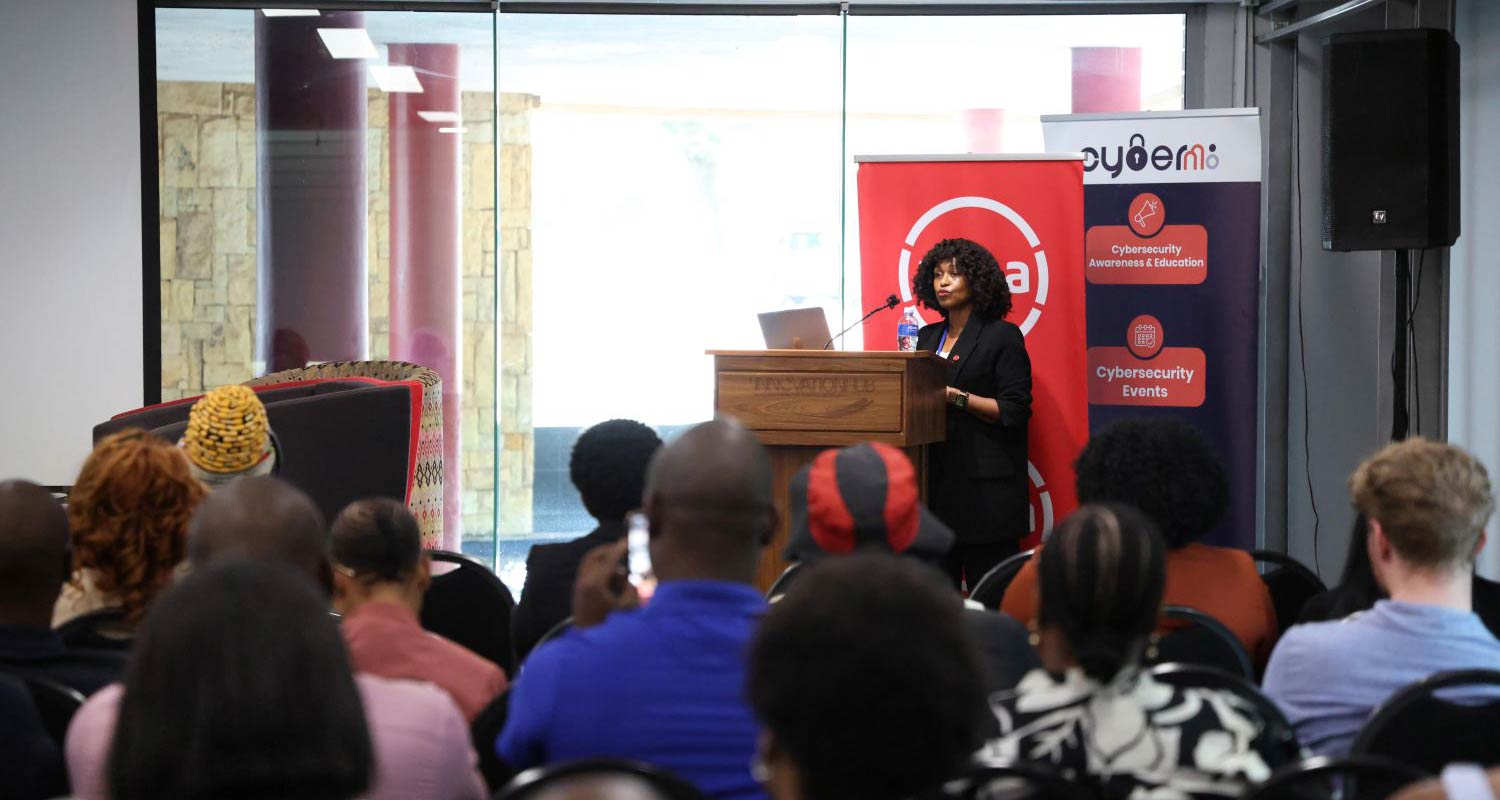
    A speaker addresses delegates at a CyberM8 Initiative cybersecurity awareness event at The Innovation Hub. The regulation of cybersecurity service providers will be discussed at the Africa Cybersecurity Indaba 2026 in Johannesburg this October. Image: Lerato Sepotokele/DCDT
    A speaker addresses delegates at a CyberM8 Initiative cybersecurity awareness event at The Innovation Hub. The regulation of cybersecurity service providers will be discussed at the Africa Cybersecurity Indaba 2026 in Johannesburg this October. Image: Lerato Sepotokele/DCDT

    At the Africa Cybersecurity Indaba 2026, co-hosted by CyberM8 Initiative NPC and the department of communications & digital technologies, the regulation of cybersecurity service providers will form part of this broader conversation.

    More than 750 leaders, policymakers, regulators, cybersecurity professionals, technology executives, researchers and other stakeholders from across Africa are expected to gather in Johannesburg in October.

    We don’t expect everyone in the room to agree. In fact, they probably shouldn’t. The purpose of dialogue is not to arrive with the answer already written. It is to make sure that the people who will be affected by the answer have an opportunity to shape it.

    Africa needs cybersecurity providers that can be trusted. It also needs a cybersecurity industry that can grow, innovate, create jobs and give emerging African companies an opportunity to compete.

    How we achieve both may be one of the most important cybersecurity policy conversations we need to have. And perhaps that is where the answer to who secures the securers? should begin.

    • Read more articles by CyberM8 on TechCentral
    • This promoted content was paid for by the party concerned
    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    CyberM8 INTIC PSiRA Sizwe Snail ka Mtuze Snail Attorneys
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleWhy school fees keep rising faster than inflation
    Next Article How AI voice reduces cost and improves performance in South African contact centres

    Related Posts

    Digital sovereignty on the agenda at Africa Cybersecurity Indaba

    Digital sovereignty on the agenda at Africa Cybersecurity Indaba

    18 August 2026
    Add A Comment

    Comments are closed.

    Company News
    How to choose a .co.za domain without paying more later

    How to choose a .co.za domain without paying more later

    20 October 2026
    Winners, from left: Zandile Monaisa (Rand Refinery), Sibongakonke Kheswa (PSG Capital), Stefan Links (Forestry South Africa), Thabang Modiba (Mondelez International), Charmaine Ncube (Razor PR), Shaun Burger-Smal (Bestmed Medical Scheme), Nandipha Ngcobo (Transnet), Tracy Mulwela (Vodacom), Cheryl-Lynn Freeman (Mzansi Business Services), Yasheen Harrielall (Zutari), Valentine Mabaso (Taonga Business Group) and Thabang Thlaku (African Rainbow Minerals). Image: Rising Star Awards

    Celebrating South Africa’s rising stars: the leaders shaping what comes next

    19 October 2026
    Paratus Zambia delivers Starlink to thousands of children in Family Legacy schools

    Paratus Zambia delivers Starlink to thousands of children in Family Legacy schools

    15 October 2026
    Opinion
    Nonkqubela Thathakahle Jordan-Dyani

    Why cybersecurity is now a national security issue for South Africa

    15 October 2026
    When a machine can choose, who does it become? Fanie van Rooyen

    When a machine can choose, who does it become?

    9 October 2026
    Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

    Let South Africans jailbreak their way to digital sovereignty

    5 October 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    How to choose a .co.za domain without paying more later

    How to choose a .co.za domain without paying more later

    20 October 2026
    Most of Datatec's R7-billion payout was taken in shares, not cash

    Most of Datatec’s R7-billion payout was taken in shares, not cash

    20 October 2026
    This is what an AI-run hacking spree looks like

    This is what an AI-run hacking spree looks like

    20 October 2026
    Post Office wants R2.2-billion from government as it braces for another loss

    Post Office wants R2.2-billion from government as it braces for another loss

    19 October 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter