Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      DJ Zinhle is launching a mobile network for her 'besties'

      DJ Zinhle is launching a mobile network for her ‘besties’

      3 November 2026
      Telcos push for 20-Sim cap and accuse Icasa of overreach - ACT CEO Nomvuyiso Batyi

      Telcos push for 20-Sim cap and accuse Icasa of overreach

      3 November 2026
      Race opens to run South Africa's .co.za domain

      Race opens to run South Africa’s .co.za domain

      3 November 2026
      Pick n Pay turns to AI to speed up online orders

      Pick n Pay turns to AI to speed up online orders

      3 November 2026
      The GSMA's top three all have big bets on Africa - Airtel Africa's Gopal Vittal, Vodafone Group's Margherita Della Valle and MTN Group's Ralph Mupita

      Africa’s mobile heavyweights take charge of the GSMA

      3 November 2026
    • World
      John Ternus faces first big test as Apple CEO - John Ternus

      John Ternus faces first big test as Apple CEO

      2 November 2026
      Alleged Israeli spy company heavily targeted Starlink users

      How online ads were used to hunt Starlink users

      28 October 2026
      Anthropic's IPO stands alone

      Anthropic’s IPO stands alone

      23 October 2026
      PHP flaws trigger global scramble as hackers pounce

      PHP flaws trigger global scramble as hackers pounce

      22 October 2026
      OpenAI turns the tables on Apple in trade secrets fight

      OpenAI turns the tables on Apple in trade secrets fight

      15 October 2026
    • In-depth
      Why investors are souring on Netflix

      Why investors are souring on Netflix

      22 October 2026

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
      Google DeepMind CEO Demis Hassabis. Image: John Sears

      The plan to stop AI from breaking the world

      16 July 2026
      The internet has a Strait of Hormuz problem

      The internet has a Strait of Hormuz problem

      15 July 2026
    • TCS
      TCS+ | Vox on AI, data rules and omnichannel communication for SMEs

      TCS+ | Vox on AI, data rules and omnichannel communication for SMEs

      26 October 2026
      TCS | The Cape Town firm quietly connecting Eskom, Pep and 6 000 ATMs - Réan van Niekerk, Metacom

      TCS | The Cape Town firm quietly connecting Eskom, Pep and 6 000 ATMs

      23 October 2026
      TCS+ | Boards are underestimating the cost of a cyberattack, says Arctic Wolf - Jason Oehley and Andre Den Hond

      TCS+ | Boards are underestimating the cost of a cyberattack, says Arctic Wolf

      22 October 2026
      W&W | LDV's Gerhard Moolman on electric bakkies, fleet orders and 'school fees'

      W&W | LDV’s Gerhard Moolman on electric bakkies and fleets

      9 October 2026
      TCS | Frogfoot sees bigger fibre deals coming - TechCentral Show guests Abraham van der Merwe and Shane Chorley

      TCS | Frogfoot sees bigger fibre deals coming

      8 October 2026
    • Opinion
      AI's boardroom honeymoon is over - Gary Stocks

      AI’s boardroom honeymoon is over

      22 October 2026
      Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

      Before South Africa licenses Starlink, it should look at Ukraine

      21 October 2026
      Nonkqubela Thathakahle Jordan-Dyani

      Why cybersecurity is now a national security issue for South Africa

      15 October 2026
      When a machine can choose, who does it become? Fanie van Rooyen

      When a machine can choose, who does it become?

      9 October 2026
      Let South Africans jailbreak their way to digital sovereignty - Dirk de Vos

      Let South Africans jailbreak their way to digital sovereignty

      5 October 2026
    • Company News
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Fintech and payments
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » Sections » Information security » Insurers carry the can for MIP breach, regulators say

    Insurers carry the can for MIP breach, regulators say

    Three months on, the Information Regulator is still establishing how many insurers the MIP breach affected.
    By Duncan McLeod25 September 2026
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

    Insurers carry the can for MIP breach, regulators say

    More than three months after attackers took the personal information of insurance customers from software supplier MIP Holdings, the Information Regulator is still trying to establish how many insurers and policyholders were affected – and it is working that out with MIP, not the insurers.

    In a written response to questions from TechCentral, the regulator confirmed that MIP reported the breach as required under section 22 of the Protection of Personal Information Act (Popia), which deals with notifying the regulator of security compromises. It said it was engaging with MIP “to establish the circumstances that led to the breach including the number of responsible parties and data subjects that have been affected”.

    Under Popia, the responsible party is the organisation that decides why and how personal information is processed – in this case, each insurer. MIP, which processes the data on their behalf, is an operator. Data subjects are the people the information belongs to.

    The obligation rests on the responsible party in respect of the processing concerned

    “The obligation rests on the responsible party in respect of the processing concerned,” the regulator said. An operator’s duty is to tell its client “without undue delay” when it has reasonable grounds to believe personal information has been accessed or acquired by an unauthorised person.

    Asked how many notifications it had received in connection with the incident, and from whom, the regulator confirmed only MIP’s. It did not say whether any of the insurers had notified it separately. MIP CEO Richard Firth told TechCentral earlier this month that about 45 of its client organisations, almost all of them life insurers, were affected.

    The regulator declined to disclose the scope, status or substance of its investigation, including whether it extends to the insurers, saying that could prejudice the regulatory process. Its enforcement powers, it said, may be exercised against responsible parties and, where applicable, operators.
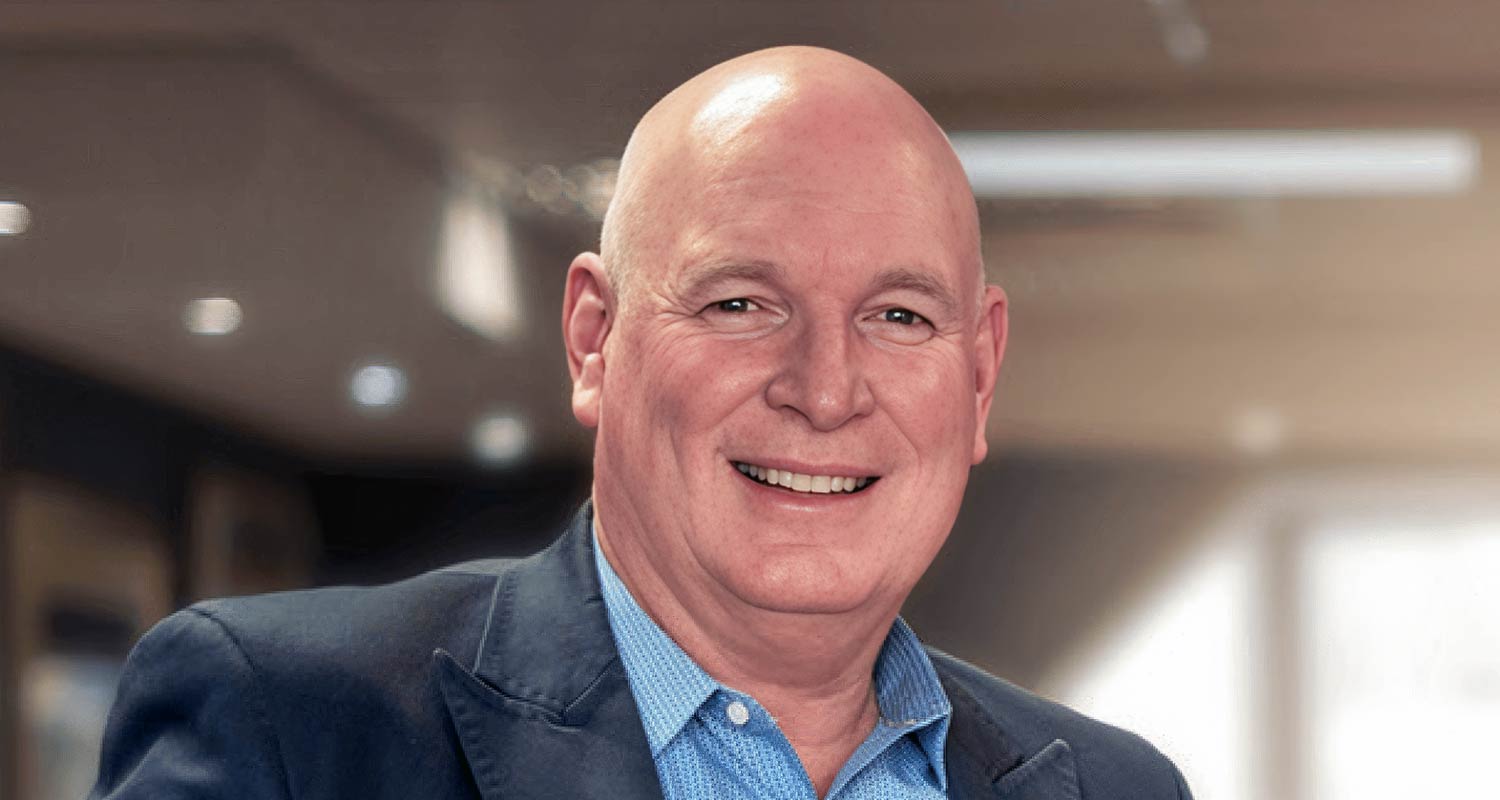
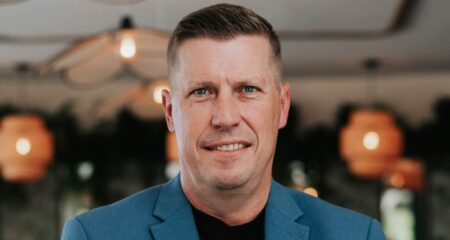
    MIP Holdings CEO Richard Firth
    MIP Holdings CEO Richard Firth

    The Prudential Authority (PA), the Reserve Bank arm that supervises insurers, said it became aware of the incident around mid-June “through information shared by certain affected supervised financial institutions”. It then sought more information from those institutions and requested a meeting with MIP.

    The PA said third-party service providers are not required to report to it directly. The obligation, again, lies with the insurers. Supervised institutions must assess incidents affecting their systems, operations or information, including those that originate at a service provider, the PA said. Where an incident is classified as material, the institution must report it to the PA within 24 hours under Joint Standard 2 of 2024 on Cybersecurity and Cyber Resilience.

    The PA would not say which insurers reported the incident, when they did so or how many reports it received, describing this as confidential supervisory information.

    Where shortcomings are identified, the PA may address them through its established supervisory processes

    Nor would it confirm Firth’s account that a meeting with the Reserve Bank concluded the breach did not pose a systemic risk. The PA said only that it and the relevant functions of the Reserve Bank monitor incidents of this kind for their potential impact on financial stability, weighing factors such as disruption to services, the containment measures taken and the potential for risk “to transmit or amplify across the sector”.

    MIP paid the ransomware group, known as The Gentlemen, a sum Firth would describe only as substantial, in exchange for an undertaking to destroy the data. The undertaking did not held. The group has since published Hollard funeral policyholders’ details on a dark web leak site, including the names of their children, identity numbers and e-mail addresses. Hollard refused a ransom demand, TechCentral has learnt.

    A ransom payment settles nothing

    Both regulators made clear that MIP’s payment changes nothing for the insurers. The Information Regulator said it could not comment on MIP’s “engagements with threat actors”, as its concern is whether responsible parties have adequate measures to protect the confidentiality and integrity of personal information. “The payment of a ransom should, however, not be understood, in itself, as either establishing or resolving compliance with Popia,” it said.

    The PA said a ransom payment “does not conclude an incident or relieve a supervised institution of its governance, risk management, notification and customer protection responsibilities”. It expects insurers caught up in a supplier’s breach to obtain assurance about containment, recovery and remediation and to assess the impact on their customers.

    Whether the Hollard leak triggers a fresh notification duty depends on the facts, the Information Regulator said, including what was known about the original compromise and whether the later publication amounts to a separate unauthorised access or acquisition. “An earlier notification does not, as a general proposition, provide a blanket exemption from subsequent obligations under Popia,” it said. Equally, a later publication does not automatically require a second section 22 notification.

    Hollard has said it notified customers affected by the June incident, is engaging with the relevant regulators and has found no evidence of compromise within its own systems.
    Ransomware

    MIP is not regulated or supervised by the PA. Yet the breach, which began when attackers used an employee’s reused credentials to reach a support platform the company was decommissioning, touched close to half its insurer clients.

    Asked how it assesses concentration risk where a single unregulated software supplier serves a large share of one sector, the PA said third-party risk management remains the responsibility of supervised institutions. It collects and analyses information on material third-party and outsourcing arrangements from those institutions once a year to identify potential concentration risks. It declined to validate MIP’s figures on how many clients were affected.

    The PA would not say whether it has closed its engagement with MIP or whether it plans any supervisory action. “Where shortcomings are identified, the PA may address them through its established supervisory processes.”  – © 2026 NewsCentral Media
    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    Hollard Information Regulator MIP Holdings Prudential Authority Richard Firth South African Reserve Bank The Gentlemen
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleSouth Africa’s car exports face an EV reckoning
    Next Article Meta’s new gadget is a pocket watch for its viral AI agent

    Related Posts

    A practical guide to attack surface management for South African organisations - Jason Oehley, Arctic Wolf

    A practical guide to attack surface management for South African organisations

    3 November 2026
    Icasa wants your fingerprint before you can get a Sim card

    Icasa wants your fingerprint before you can get a Sim card

    29 October 2026
    Rate hikes threaten a household recovery built on cheaper credit - John Gellatly

    Rate hikes threaten a household recovery built on cheaper credit

    29 October 2026
    Company News

    The commercial barriers holding back smaller ISPs

    3 November 2026
    Five cyber worries keep South African business owners up at night - Bennie Barnard, NEWORDER

    Five cyber worries keeping South African business owners up at night

    3 November 2026
    Standard Bank wins four global awards for digital banking innovation - Funeka Montjane

    Standard Bank wins four global awards for digital banking innovation

    3 November 2026
    Opinion
    AI's boardroom honeymoon is over - Gary Stocks

    AI’s boardroom honeymoon is over

    22 October 2026
    Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

    Before South Africa licenses Starlink, it should look at Ukraine

    21 October 2026
    Nonkqubela Thathakahle Jordan-Dyani

    Why cybersecurity is now a national security issue for South Africa

    15 October 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    DJ Zinhle is launching a mobile network for her 'besties'

    DJ Zinhle is launching a mobile network for her ‘besties’

    3 November 2026
    Telcos push for 20-Sim cap and accuse Icasa of overreach - ACT CEO Nomvuyiso Batyi

    Telcos push for 20-Sim cap and accuse Icasa of overreach

    3 November 2026
    Race opens to run South Africa's .co.za domain

    Race opens to run South Africa’s .co.za domain

    3 November 2026
    Pick n Pay turns to AI to speed up online orders

    Pick n Pay turns to AI to speed up online orders

    3 November 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter