Close Menu
TechCentralTechCentral

    Subscribe to the newsletter

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Facebook X (Twitter) YouTube LinkedIn
    WhatsApp Facebook X (Twitter) LinkedIn YouTube
    TechCentralTechCentral
    • News
      Nersa misses its own target for cross-border trading rules

      Nersa misses its own target for cross-border trading rules

      11 November 2026
      Lenovo's Thibault Dousson to take the top job at Tarsus

      Lenovo’s Thibault Dousson to take the top job at Tarsus

      11 November 2026
      Telkom wants Icasa's BEE rules eased for everyone, Starlink included

      Telkom wants Icasa’s BEE rules eased for everyone, Starlink included

      11 November 2026
      Vox veteran Jacques du Toit hangs up his gloves

      Vox veteran Jacques du Toit hangs up his gloves

      11 November 2026

      Jensen Huang scandal wipes $430-billion off Nvidia

      11 November 2026
    • World
      John Ternus faces first big test as Apple CEO - John Ternus

      John Ternus faces first big test as Apple CEO

      2 November 2026
      Alleged Israeli spy company heavily targeted Starlink users

      How online ads were used to hunt Starlink users

      28 October 2026
      Anthropic's IPO stands alone

      Anthropic’s IPO stands alone

      23 October 2026
      PHP flaws trigger global scramble as hackers pounce

      PHP flaws trigger global scramble as hackers pounce

      22 October 2026
      OpenAI turns the tables on Apple in trade secrets fight

      OpenAI turns the tables on Apple in trade secrets fight

      15 October 2026
    • In-depth
      Ducking hell: inside Apple's hidden list of words the iPhone won't suggest

      Ducking hell: inside Apple’s hidden list of words the iPhone won’t suggest

      6 November 2026
      Why investors are souring on Netflix

      Why investors are souring on Netflix

      22 October 2026

      10 days that changed the course of AI

      21 September 2026
      Meta to the AI industry: slow down without us - Mark Zuckerberg

      Meta to the AI industry: slow down without us

      16 September 2026
      Google DeepMind CEO Demis Hassabis. Image: John Sears

      The plan to stop AI from breaking the world

      16 July 2026
    • TCS
      TCS+ | Old Mutual's Celiwe Ross on leading people through AI - Old Mutual

      TCS+ | Old Mutual’s Celiwe Ross on leading people through AI

      6 November 2026
      TCS+ | How the Apple ecosystem drives productivity for SMEs - Sudesh Pillay iStore and Kevin McLennan

      TCS+ | How the Apple ecosystem drives productivity for SMEs

      6 November 2026
      TCS+ | Vox on AI, data rules and omnichannel communication for SMEs

      TCS+ | Vox on AI, data rules and omnichannel communication for SMEs

      26 October 2026
      TCS | The Cape Town firm quietly connecting Eskom, Pep and 6 000 ATMs - Réan van Niekerk, Metacom

      TCS | The Cape Town firm quietly connecting Eskom, Pep and 6 000 ATMs

      23 October 2026
      TCS+ | Boards are underestimating the cost of a cyberattack, says Arctic Wolf - Jason Oehley and Andre Den Hond

      TCS+ | Boards are underestimating the cost of a cyberattack, says Arctic Wolf

      22 October 2026
    • Opinion
      Icasa's Sim rules need a privacy backstop - Lloyd Matthew and Heinz Vollmer

      Icasa’s Sim rules need a privacy backstop

      5 November 2026
      AI's boardroom honeymoon is over - Gary Stocks

      AI’s boardroom honeymoon is over

      22 October 2026
      Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

      Before South Africa licenses Starlink, it should look at Ukraine

      21 October 2026
      Nonkqubela Thathakahle Jordan-Dyani

      Why cybersecurity is now a national security issue for South Africa

      15 October 2026
      When a machine can choose, who does it become? Fanie van Rooyen

      When a machine can choose, who does it become?

      9 October 2026
    • Company News
      • 1Stream
      • Africa Data Centres
      • AfriGIS
      • Altron Digital Business
      • Altron Document Solutions
      • Altron Group
      • Arctic Wolf
      • Ascent Technology
      • AvertITD
      • BBD
      • Braintree
      • CallMiner
      • CambriLearn
      • CM.com
      • Contactable
      • CYBER1 Solutions
      • Digicloud Africa
      • Digimune
      • Domains.co.za
      • ESET
      • Euphoria Telecom
      • HOSTAFRICA
      • Incredible Business
      • iONLINE
      • IQbusiness
      • Iris Network Systems
      • Kaspersky
      • LSD Open
      • Mitel
      • NEC XON
      • Netstar
      • Network Platforms
      • Next DLP
      • Ovations
      • Paracon
      • Paratus
      • Publishared
      • Q-KON
      • SevenC
      • SkyWire
      • Solid8 Technologies
      • Telit Cinterion
      • Telviva
      • Tenable
      • Vertiv
      • Videri Digital
      • Vodacom Business
      • Vox
      • Wipro
      • Workday
      • XLink
    • Sections
      • AI and machine learning
      • Banking
      • Broadcasting and media
      • Cloud services
      • Contact centres and CX
      • Cryptocurrencies
      • Education and skills
      • Electronics and hardware
      • Energy and sustainability
      • Enterprise software
      • Fintech and payments
      • HealthTech
      • Information security
      • Internet and connectivity
      • Internet of things
      • Investment
      • IT services
      • Lifestyle
      • Policy and regulation
      • Public sector
      • Retail and e-commerce
      • Satellite communications
      • Science
      • SMEs and start-ups
      • Social media
      • Talent and leadership
      • Telecoms
      • Watts & Wheels
    • Events
    • Advertise
    TechCentralTechCentral
    Home » In-depth » Ashley Madison and the rise of the moralist hacker

    Ashley Madison and the rise of the moralist hacker

    By The Conversation22 July 2015
    Twitter LinkedIn Facebook WhatsApp Email Telegram Copy Link
    Get breaking news on WhatsApp

    ashley-madison-640

    There’s value in more than just credit card data, as Avid Life Media (ALM), parent company of the extramarital affair website Ashley Madison, has found out after being raided for millions of their customer’s details.

    All sorts of information that isn’t expressly financial is valuable — HR records including personal information and health information, such as those stolen from the US government, can be used to fraudulently gain access to other data, or for blackmail for financial gain or to further a political or moral agenda.

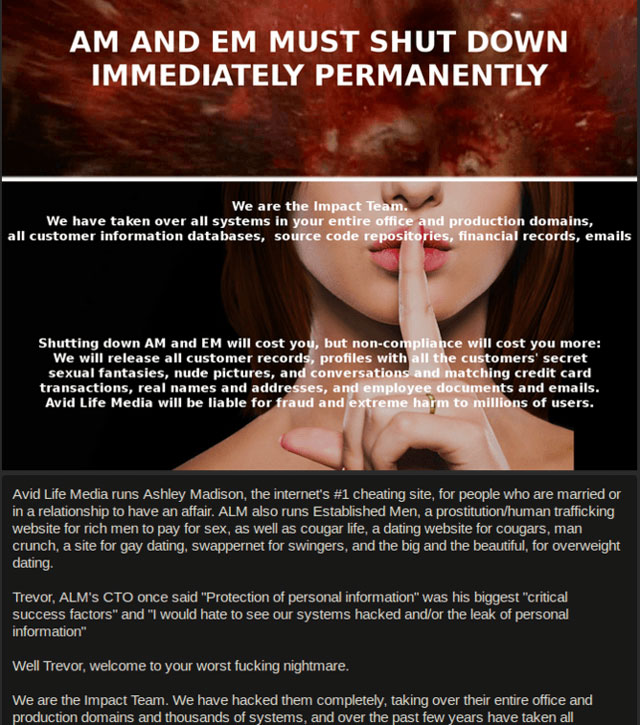
    The Ashley Madison hackers, calling themselves Impact Team, seem to have a moral agenda, adding another dimension to the factors that motivate cybercriminals, and therefore something else for overburdened security professionals to consider.

    There is a spectrum of sensitive information, from an e-mail address to private secrets. The theft of the Ashley Madison databases, essentially a list of 37m possible adulterers’ identifying details, must rank as one of the most “sensitive” troves of data ever acquired. While there will be credit card details too, it’s the potential for public (and private) embarrassment that many will be fearing.

    Reported by security research Brian Krebs and confirmed by ALM CEO Noel Biderman, Impact Team’s statement rails against the motivations not just of the supposed cheaters using the site, but the site itself for facilitating this behaviour, demanding that ALM close down Ashley Madison and another of its sites, Established Men, permanently or risk the details being published.

    Impact Team’s ire is directed particularly at ALM’s “full delete” service where, for US$19, all a user’s details will be deleted. They claim ALM made $1,7m from this service, yet leave the credit card details, obviously including real names and addresses, intact. Impact Team hint that the hack was made possible through an insider — embarrassing for a firm that had aimed to raise $200m this summer from an IPO.

    According to a recent survey by Thales, typically the most sensitive data that is encrypted is employee and HR data. It goes without saying that this is highly sensitive information that can bring repercussions both on the individuals and the firm in question. As customers, we may not be pleased to note that customer details are some way down the list. Really, all these aspects should be closer to 100%.

    Intellectual property is certainly a target for cyberattacks, with the loss of source code and secret product information potentially disastrous for companies. Hacking Team recently found the internal code of their commercial hacking tools posted all over the Internet, for example.

    When university researchers analysed 300 discarded hard disk drives they found that a third contained personal data including health and banking information (including a €50bn currency exchange service), and even details for a missile defence system. The lack of planning and care in how this information was dealt with is astonishing.

    Poking the hornet’s nest
    The catastrophic raid on Sony’s corporate network last year was blamed on North Korea, but Sony has battled Anonymous, Lulzsec and Lizard Squad over the years, often over their stance on breaches of copyright. Again, a disgruntled insider within Sony is the most likely source of the breach. The hack led to all manner of documents appearing online — such as embarrassing e-mails from senior executives.

    Sony’s trouble with hacking organisations can be traced to its court case against George Holtz, who Sony sued after he published root encryption keys for the PlayStation console. Sony demanded identifying details of visitors to his website and social media pages, and was given access to Holtz’s PayPal account. The case judge eventually granted Sony permission to view IP addresses of everyone who visited Holtz’s site, geohot.com. In April 2011, Sony settled the lawsuit out of court, but have since faced many further attacks.

    The fact is hackers are increasingly pursuing a variety of agendas. In protest at St Louis County Police involvement in the death of unarmed teenager Michael Brown in Ferguson, Missouri, the police department’s website was attacked, knocking it offline for several days. The group responsible declared they had gained access to dispatch tapes related to the day of the shooting, which they then uploaded to YouTube.
    The message left by Hacking Team
    The message left by Impact Team

    In political actions worldwide, from the Arab Spring uprising, to Russia’s suspected cyberattacks on Estonian government websites, or the Syrian Electronic Army, the Internet is increasingly a new vector of attack. The Internet as battleground is not in the future, it is already here, and as attack on the French channel TV5Monde should remind us, it may escalate to include control of news outlets, too.

    Organisations need to understand that there are new risks and new ways to distribute messages, especially from those skilful enough to disrupt traditional methods. It’s important to note that the viewpoint of the hacktivist will often be reflected in the political landscape of the time, and that this is subject to change. The hacktivist, a cybercriminal to some, can be a freedom fighter to others.

    The Internet provides a voice for all, and there are many examples where corporations, organisations or governments have outraged groups around the world who have successfully staged an uprising or retaliation against them. Someone may be small on the Internet, but can still have a massive impact. Sony lost billions of dollars from its share price, and forfeited a great deal of customer confidence.

    A strong defence is the starting point, but if there is trusted internal access then it is possible to circumvent the locks. With digital media cards now supporting hundreds of gigabytes of data it’s not too difficult to take huge amounts of data off-site — and this is why encryption is so vital. In short:

    • Encrypt sensitive data
    • Control and limit access to sensitive data
    • Make sure those controls work
    • Check who has access to the data
    • Integrate multi-factor authentication for the access to sensitive information
    • Watch where you back up your data and protect that, too
    • Don’t use the same encryption keys for everything

    And finally, try not to upset people. Ashley Madison rashly boasted of its superior security, while flaunting what many would describe as unethical behaviour. Such things are red rags to a bull. Companies need to understand that their insecurity today is as much to do with their behaviour and the reactions or political and social aims of others in response as it is the straightforward quest for financial gain.The Conversation

    • Bill Buchanan is head, Centre for Distributed Computing, Networks and Security at Edinburgh Napier University
    • This article was originally published on The Conversation
    Add TechCentral as a preferred source on GoogleFollow TechCentral on Google NewsGet breaking news on WhatsApp


    ALM Ashley Madison Bill Buchanan
    WhatsApp YouTube
    Share. Facebook Twitter LinkedIn WhatsApp Telegram Email Copy Link
    Previous ArticleAdvtech rejects Curro’s advances
    Next Article How crooks steal your identity

    Related Posts

    Bitcoin’s moment of reckoning arrives

    28 April 2016

    The cloud isn’t as robust as we think

    1 October 2015

    How to create a bulletproof password

    31 August 2015
    Company News
    Coen Jonker receives the Lifetime Achievement Award at the inaugural SA FinTech Awards in 2025, presented by Darren Franks, CEO of Finasa

    Finasa’s SA FinTech Awards: banks and fintechs, building together

    11 November 2026
    The hidden risks of fragmented IT and unenforced SLAs - ITC Systems Durban

    The hidden risks of fragmented IT and unenforced SLAs

    10 November 2026
    Why AI-powered customer experience will decide South Africa's festive retail winners - CM.com

    Why AI-powered customer experience will decide South Africa’s festive retail winners

    10 November 2026
    Opinion
    Icasa's Sim rules need a privacy backstop - Lloyd Matthew and Heinz Vollmer

    Icasa’s Sim rules need a privacy backstop

    5 November 2026
    AI's boardroom honeymoon is over - Gary Stocks

    AI’s boardroom honeymoon is over

    22 October 2026
    Before South Africa licenses Starlink, it should look at Ukraine - Duncan McLeod

    Before South Africa licenses Starlink, it should look at Ukraine

    21 October 2026

    Subscribe to Updates

    Get the best South African technology news and analysis delivered to your e-mail inbox every morning.

    Latest Posts
    Coen Jonker receives the Lifetime Achievement Award at the inaugural SA FinTech Awards in 2025, presented by Darren Franks, CEO of Finasa

    Finasa’s SA FinTech Awards: banks and fintechs, building together

    11 November 2026
    Nersa misses its own target for cross-border trading rules

    Nersa misses its own target for cross-border trading rules

    11 November 2026
    Lenovo's Thibault Dousson to take the top job at Tarsus

    Lenovo’s Thibault Dousson to take the top job at Tarsus

    11 November 2026
    Telkom wants Icasa's BEE rules eased for everyone, Starlink included

    Telkom wants Icasa’s BEE rules eased for everyone, Starlink included

    11 November 2026
    © 2009 - 2026 NewsCentral Media
    Built and maintained by Chronon
    • Cookie policy (ZA)
    • TechCentral – privacy and Popia

    Type above and press Enter to search. Press Esc to cancel.

    Manage consent

    TechCentral uses cookies to enhance its offerings. Consenting to these technologies allows us to serve you better. Not consenting or withdrawing consent may adversely affect certain features and functions of the website.

    Functional Always active
    The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
    Preferences
    The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
    Statistics
    The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
    Marketing
    The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
    • Manage options
    • Manage services
    • Manage {vendor_count} vendors
    • Read more about these purposes
    View preferences
    • {title}
    • {title}
    • {title}
    🇿🇦 Sign up to the TechCentral newsletter